Загрузка видео...
Не удалось загрузить видео
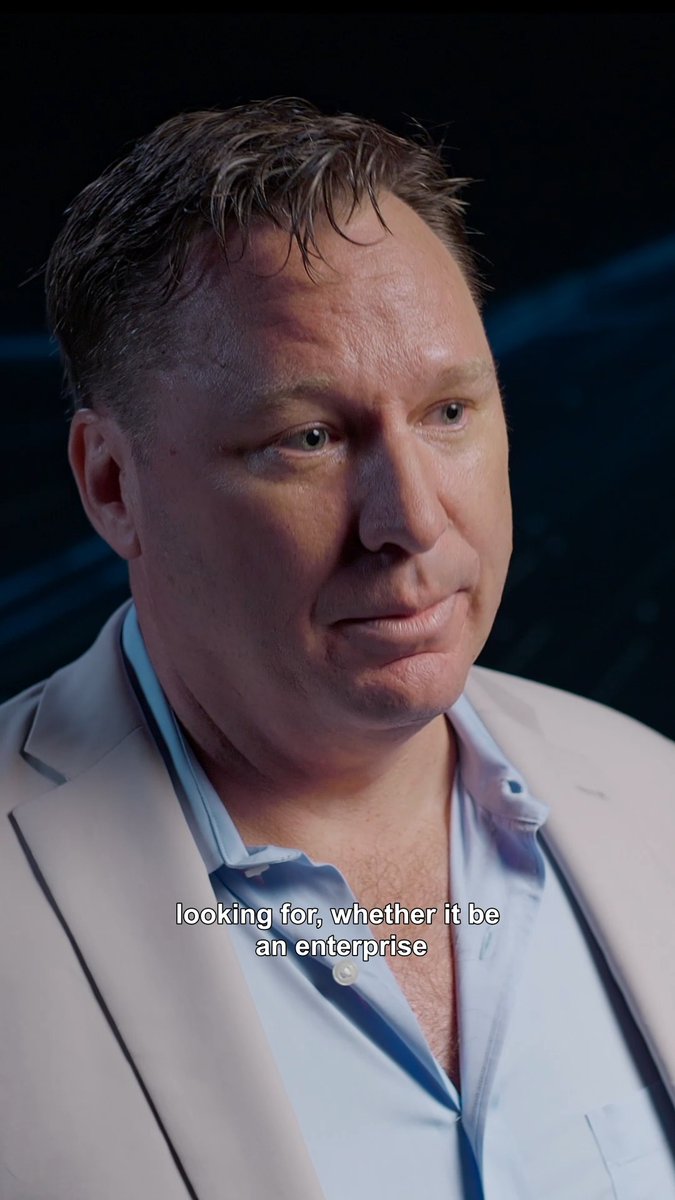
"All untrusted third-party data is now executable malware.” Sam Watts of Lakera AI discusses the challenges of securing LLM deployments against vulnerabilities like prompt injections and jailbreaks, especially in an evolving threat landscape.
470,622 просмотров • 1 год назад •via X (Twitter)
Комментарии: 27

@SamuelDWatts @LakeraAI "Untrusted third-party data is now executable malware." Bold, but absolutely correct for LLMs.

@LakeraAI Follow us for AI safety insights And watch the full video

@SamuelDWatts @LakeraAI Spot on. Treating all third‑party inputs as potentially hostile is the only sane default in LLM security. Prompt injections and jailbreaks aren’t edge cases anymore—they’re the threat landscape. Secure-by-design needs to become the norm, not the exception.

@SamuelDWatts @LakeraAI Thats a little "FAR" fetched

@SamuelDWatts @LakeraAI 🤩

@SamuelDWatts @LakeraAI Absolutely. Treat every user string like untrusted code. Sanitising and gating inputs can stop most prompt injection attempts — we found ~70% of exploits die with a simple filter. How are you layering defences today? ☺

@SamuelDWatts @LakeraAI Add CBDC and digital ID and it becomes a (blackhat) hacker’s paradise.

@SamuelDWatts @LakeraAI Critical security awareness for AI systems.

This is the exact wake-up call the industry needs. We're rushing to integrate LLMs into production without thinking about attack surface. Every RAG system, every agent with web access, every chatbot reading PDFs - all potential entry points. Prompt injection isn't a bug, it's a fundamental architectural flaw we haven't solved yet.

@SamuelDWatts @LakeraAI All spam posts on x need to go #nospam

@SamuelDWatts @SamuelDWatts 👏👏

@SamuelDWatts @LakeraAI "Executable malware" hits hard, what's your go-to for gating third-party data before it hits the LLM?

@SamuelDWatts @LakeraAI AI prompt engg is future

@SamuelDWatts @LakeraAI Interesting. This may cause traditionally-coded websites to also become AI-driven in order to protect themselves against AI-based hacking.

@SamuelDWatts @LakeraAI @grok make transcript of that video

@SamuelDWatts @LakeraAI Thoughts @BrianRoemmele?

@SamuelDWatts @LakeraAI to be honest this was already essentially the case even absent an LLM if you're presuming it's malware simply because it's untrusted, that doesn't change whether or not an LLM could be the target vector

@SamuelDWatts @LakeraAI I do think we should be cautiuous with our data being given to china or india, those people could easily exploit us and give themselves a very large very big advantage

@SamuelDWatts @LakeraAI good work

@SamuelDWatts @LakeraAI Men da ikke svære at afsløre.

@SamuelDWatts @LakeraAI whats on his arm?

@SamuelDWatts @LakeraAI Ki fogja ezekért vállalni a felelősséget?

@SamuelDWatts @LakeraAI Absolutely, Farai, that's a scary thought, but a crucial point to ponder, isn't it?

@SamuelDWatts @LakeraAI

@SamuelDWatts @LakeraAI Very thanks for this valuable content.

@SamuelDWatts @LakeraAI not if u run LLM in browser. it doesnt get execute permission there but does get GPU

@SamuelDWatts @LakeraAI You look jewish