正在加载视频...

视频加载失败

Android Universal Root Rooting Pixel 6 and 7 Pro running Android 13 👇 Analysis and Exploitation of CVE-2023-20938 (exploit a use-after-free vulnerability to elevate privileges to root and disable SELinux) [blog] [slides]
21,774 次观看 • 2 年前 •via X (Twitter)

5 条评论

Kristijan 的头像
Kristijan2 年前

Patched in Android 14?

Mobile Hacker 的头像
Mobile Hacker2 年前

patched for any Android OS version that received February 2023 security patch, not just 14

DismaltheDeveloper 的头像
DismaltheDeveloper2 年前

Even Verizon devices?

Jorge Pezo 的头像
Jorge Pezo2 年前

Is it possible to do the test on a real mobile phone?

Mobile Hacker 的头像
Mobile Hacker2 年前

If you have exploit, then yes. However, exploit is not published, because of that I don't think so

相关视频

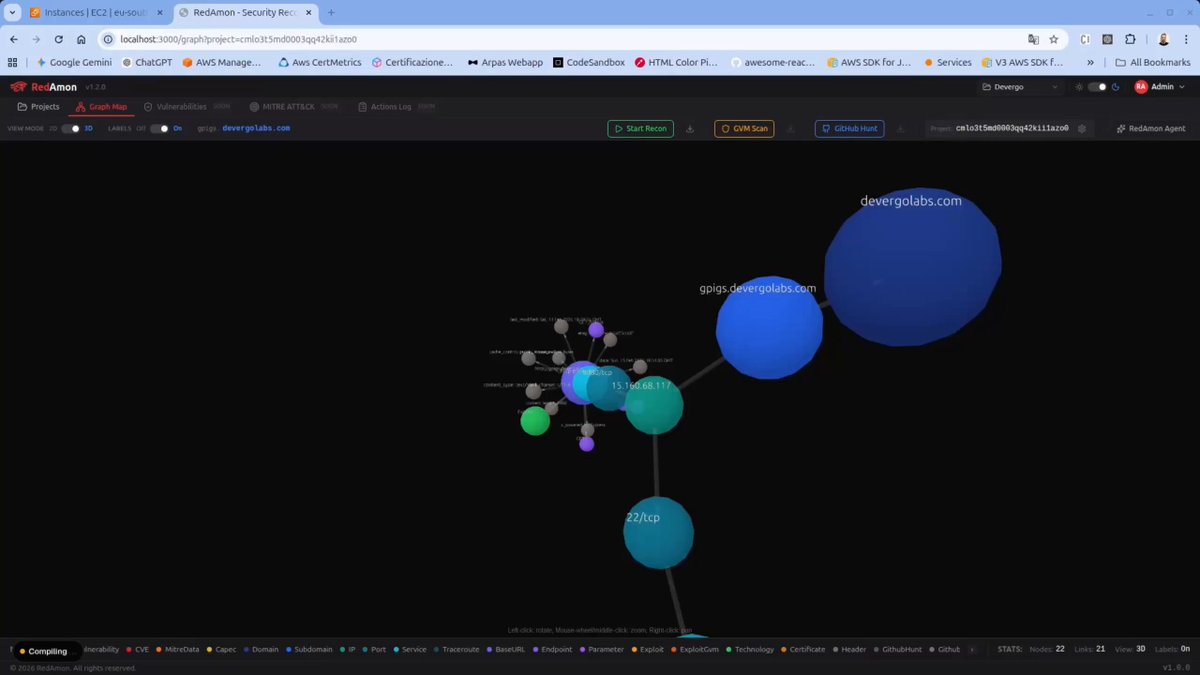
someone built an AI RED TEAM that maps your entire attack surface as a knowledge graph, finds every vulnerability, then EXPLOITS them to root access AUTONOMOUSLY its called RedAmon, 9,000 templates. 17 node types, actual Metasploit shells, not reports, no pentesters needed 6 phases of autonomous recon: subdomain discovery, port scanning, http probing, resource enumeration, vulnerability scanning, MITRE mapping every finding stored in a Neo4j graph with 17 node types and 20+ relationship types. the AI reasons about the graph, finds attack paths, and runs actual Metasploit exploits, actual shells stress-tested with zero vulnerability data, zero exploit modules, one instruction find a CVE and exploit it, it went from empty database to root-level RCE in 20 steps, researched the exploit on the web, crafted a custom deserialization payload, debugged itself when the first attempt failed next try, the server responded with root access, the highest privilege level on any Linux system. full control over everything the target was running node-serialize 0.0.4, a package with a critical deserialization flaw (CVE-2017-5941, CVSS 9.8), the server takes your cookie, decodes it, and passes it straight into unserialize() which executes any code inside it, the AI figured this out on its own with no hints built on LangGraph + MCP tool servers for naabu, nuclei, curl, metasploit. hunts leaked secrets across GitHub repos, 40+ regex patterns for AWS keys, Stripe tokens, database creds

chiefofautism

70,352 次观看 • 7 个月前