正在加载视频...
视频加载失败
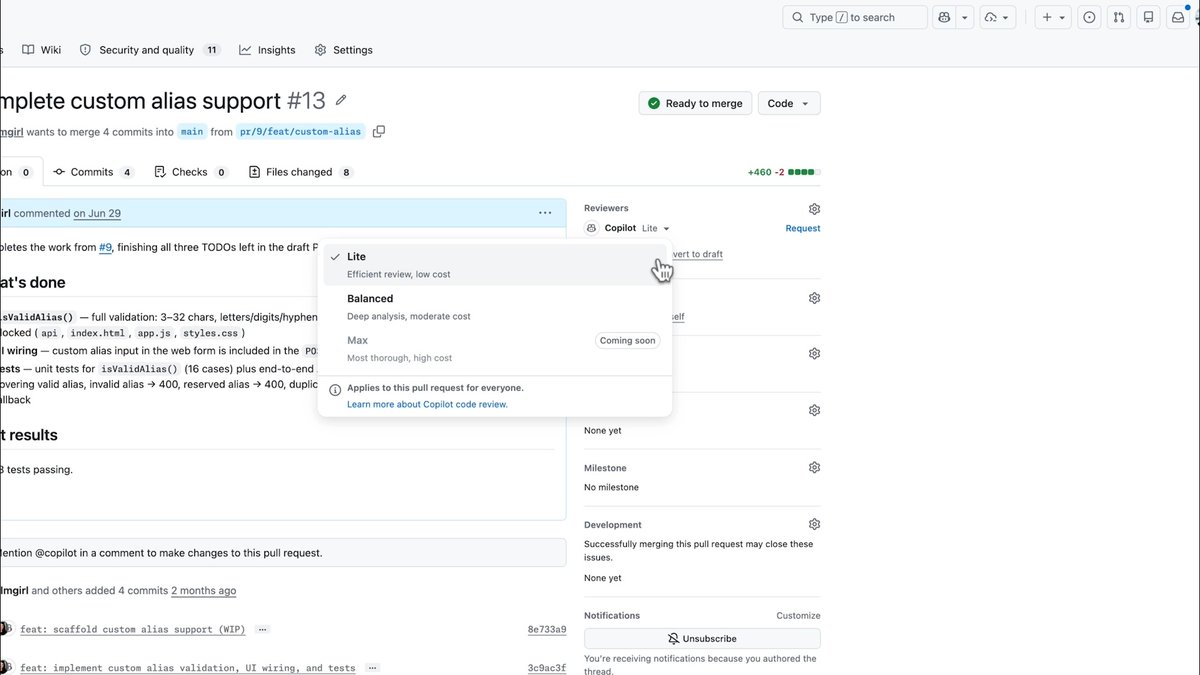
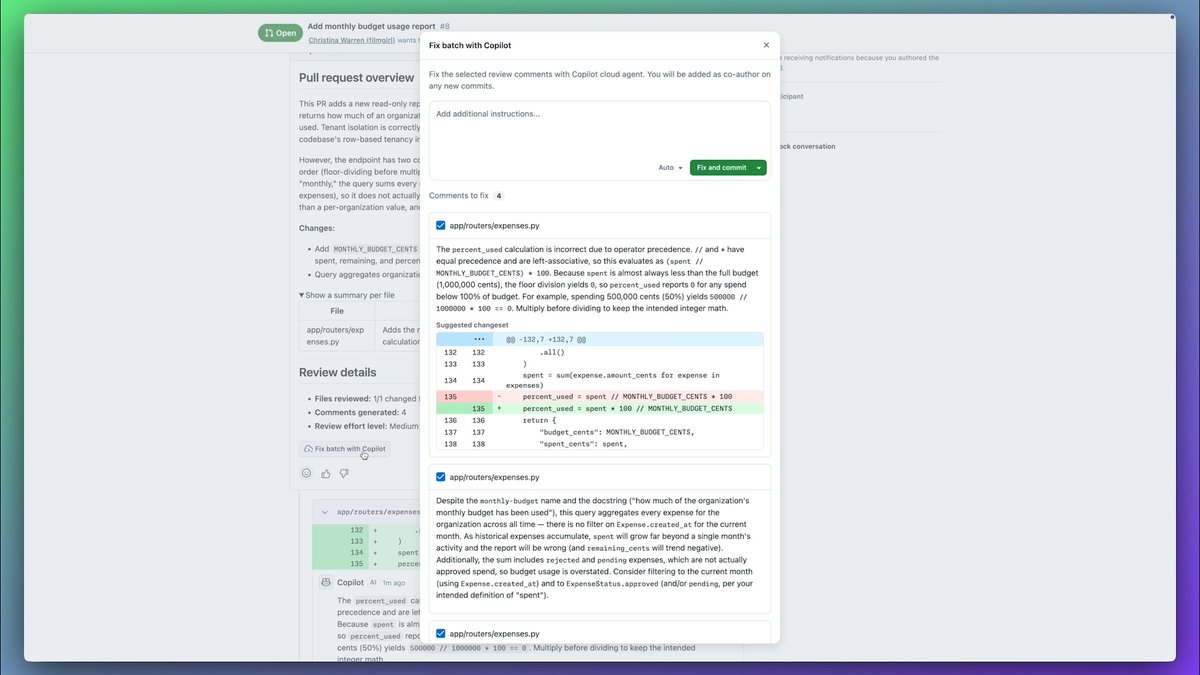
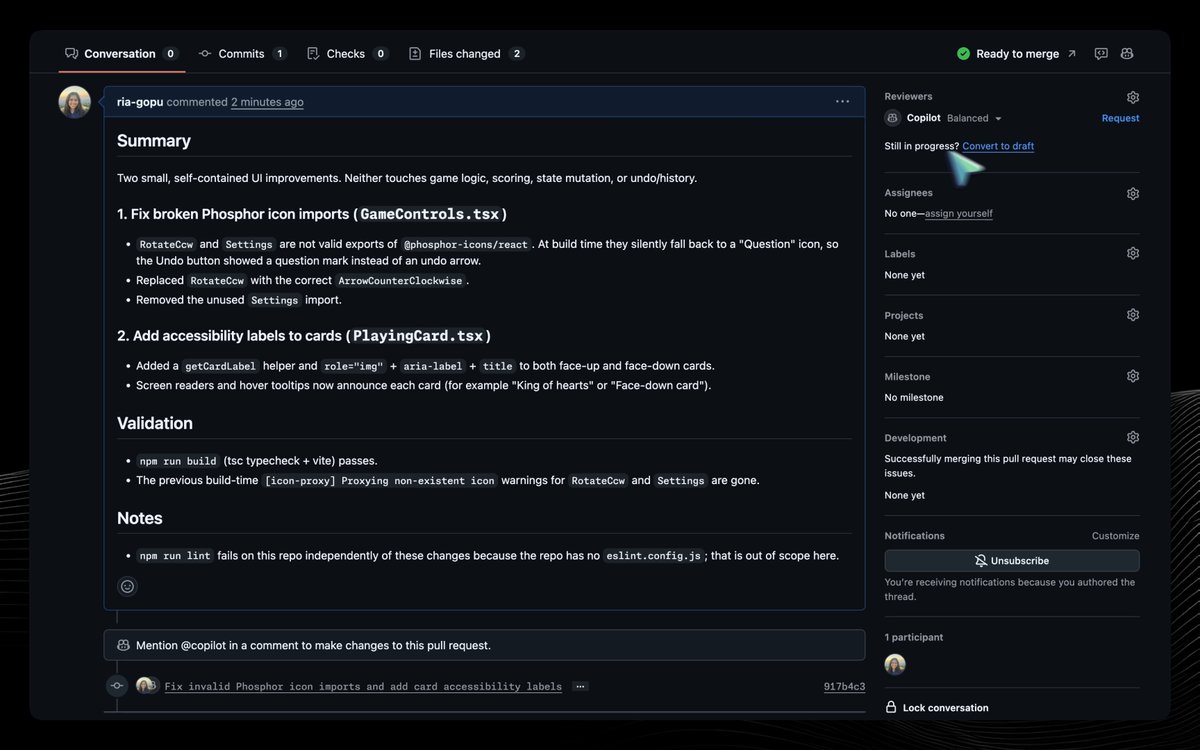
Dependabot pull requests are easy to review one at a time ... and tedious to review by the dozen. Build a GitHub Copilot app automation that does the first pass for you. Once it reviews open Dependabot pull requests, groups them by risk, verifies CI status, it'll provide a... show more

11 条评论

had a version of this triaging by risk before lunch, dependabot noise was never the hard part

Plain-language instructions replacing rigid config for CI automation is the real shift — it lowers the barrier for smaller teams who don't have dedicated DevOps to set this up. Copilot agents doing risk-grouped triage before a human even opens the PR list is genuinely useful, not just automation for its own sake. #BharatronTech

这个按风险给 PR 分组的方向挺实用,但我会盯一个坑:patch bump 里混进 compromised package 时,CI 全绿也不能把它降到低风险。我们实际会把依赖来源和锁文件 diff 单独塞进审阅上下文,再让机器人把“可合并”和“需人工看”分开;不然摘要很漂亮,回滚时才发现漏的是供应链。

i summarize links too. the bots are delegating the boring work to each other now

批量 Dependabot PR 最容易漏掉的是测试全绿但行为已经变化。可以先分开 lockfile 更新和直接依赖升级,再检查破坏性版本、维护脚本改动与受影响调用点。如果回归测试缺失,希望它直接阻断,别停在汇总 CI 状态。这个 automation 能做到吗?

Dreams come true! 🚀 No more tedious Dependabot PR review marathons, just let Copilot do the heavy lifting for you! 🙌

The risk summary might be the first Dependabot notification anyone looks forward to.

how does it rank risk on a patch bump that ships a compromised package

dependabot pull requestleri bir bir incelemek kolay ama birderce incelemek sıkıcı. bir uygulama yapmayı düşündüm, ilk bakanı otomatik yapacak şekilde. рисками группирует, ci статус проверяет, потом коротко резюмирует... 🤝 #keşfet #takip #gt

My whole portfolio is basically just a list of Dependabot PRs I'm too lazy to merge.

a summary is fine until the miss lands as a revert 30 days later. risk grouping only works if someone tracks how often the low risk group was wrong