正在加载视频...
视频加载失败
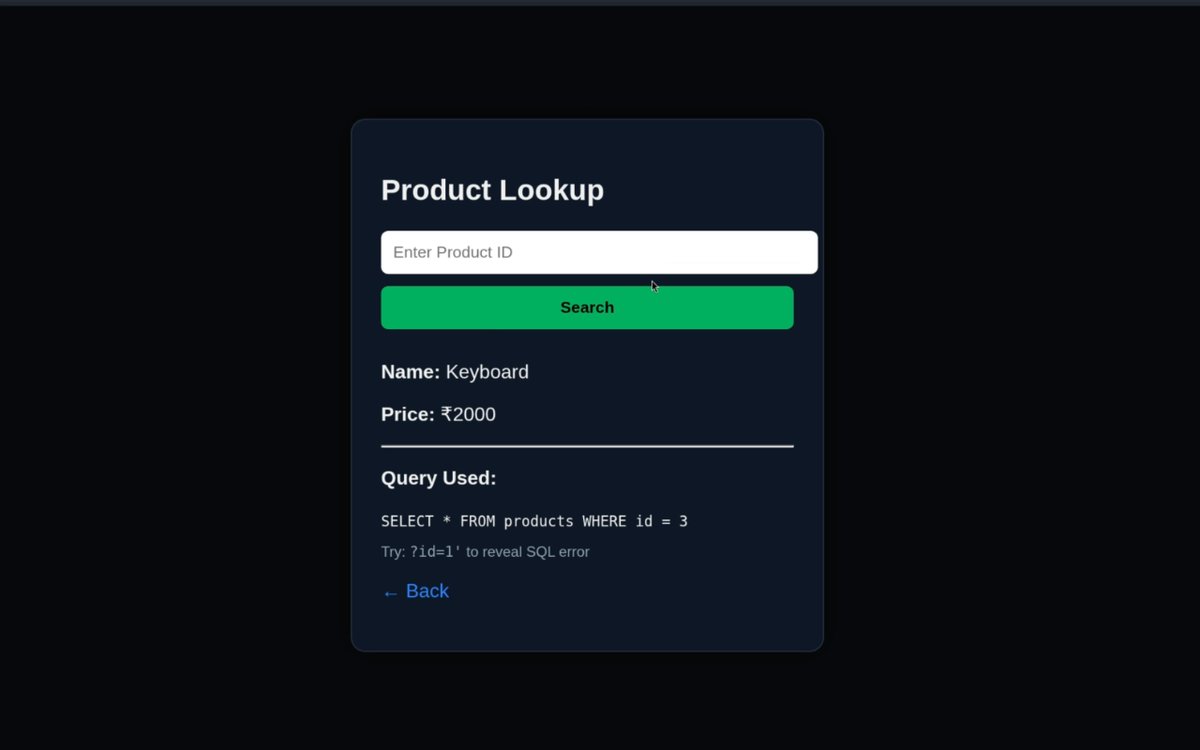
SQL INJECTION (Login page bypass)

45 条评论

Brother, no one saves database credentials in sql database nowadays.

It’ll surprise you

@Dipak_R_Dutta All of us do save db credentials in databases. Wtf are you talking about!? Have you seen corporate software in your life? 😁
@cyber_razz We use parameterized queries along with object relational mapping tools like hibernate to defend against this kind of sql injection. that kind of a context in this kind of scenario.

@Johnny7xp @cyber_razz Hibernate would go to a database no?
@Johnny7xp @cyber_razz Yes it will go to db but parameterized queries will be used so sql injection will not happen.
@Johnny7xp @cyber_razz So then creds are stored in the db?
@Johnny7xp @cyber_razz Yes in some cases but preferable way is to store one way hashed password along with salt.

if (sha256(rowusercode + POST password) === rowpassword) + (random code === post random) bypass this !!
Idk how this got to the wrong side of twitter The post is just an intro to sql injection in cases of injectable username input field

These things are blocked using most ORMs. And who builds a website without enforcing password as requirement.

If this works, the app was already broken.
Heavily
😁🤭

NEVER name your admin user admin 🤦🏻♂️

Literally no one implements auth this way anymore. I mean, direct user input to SQL query? Lol.

In this 2025 ? 😂

Still living in 2010?

The reason why you should validate and sanitize all inputs. Most Dev ignore doing that.

Yes, but 25 years ago

Welcome in 1998

@thegreatone444
This post seems like it’ll do wonders, as you drop ur take good or bad.. check me out on tiktok

The solution to this problem is to start your SQL query with the password instead of the username to authenticate the user. /s

That's why prepared statements were invented.

make one with that 1=1 on the user/password field thats one way to enter that could still get us to juicy pages!

prepared statements ... and injection are impossibile

Use Knex

Baba

this is why using ORM is recommended for web dev.

who authenticates like this? 🤣

WTH is the plain password even stored ?

This is no longer a thing as most website use strong sanitisation and input validation to prevent this.

Only newbies who create sql outside the database do those mistakes.

use prepared statements so data is sent separately from SQL logic, then escape only when rendering output, not earlier. SQLI impossible

Just do a YouTube channel at this point
I’m working on it (this particular video isn’t mine though ) But I have a lot of tutorials I’d love to make in the future
I like your consistency though

if this is the true the sql is a veeery stupid language

Lol😂😂😂

Please bye-pass this if you can built the BE + Infrastructure from A-Z.

😂😂

Learn to build in PHP a website from scratch...

Nicely explained especially with the code reference.

SQL injection in 2025 ? Eiii a well