正在加载视频...

视频加载失败

“Why Seed Phrase Wallets Keep Getting Hacked — and What Comes Next” Most people think their cold wallet is safe. Most people are wrong. Soft wallets & hardware wallets that use seed phrase backups like Ledger, Trezor, Tangem etc. all have publicly known attack vectors. Let's break them down...

808,955 次观看 • 9 个月前 •via X (Twitter)

0 条评论

暂无评论

原始帖子的评论将显示在这里

相关视频

YOUR HARDWARE WALLET SUCKS. PERIOD. ZachXBT just said what we've known for years: hardware wallets are garbage. We won't go as far but we surely feel they are not for everyone. They are for advanced users and by no means for wallets that are meant to be accessed frequently. There is one thing hardware wallets are good at: that is keeping crypto secure if someone physically trying to rip private keys (those that give you access to crypto) out of the chip. The reality is that attack almost never happens!😀 When it comes to the attacks that actually drain wallets, hardware wallets make them worse: >> 1. NOT DISCREETE The moment someone sees that little device, you're a confirmed high-value target. >> 2. LEAKED EMAILS AND ADDRESSES Buying one doxxed thousands of people. Leaked customer databases with the real names and home addresses. You just joined a phishing hit list. Emails targeting hardware wallet owners are now so convincing that even veterans get fooled. Privacy can't fail harder than that. >> 3. PAPER BACKUPS You still write your keys on paper. The seed phrase backup negates the entire point of the device. BTW, mobile wallets already moved on: Unstoppable now has passkey wallets allowing to create and restore with zero seed phrase, secured by your device. That will likely become the golden standard in the future. >> 4. YOUR PHONE ALREADY HAS A VAULT Your phone is designed for security. There's a state of the art secure storage chips in your pocket already. Apple and Google built isolated secure elements to guard the most sensitive data in your life. If integrated right by the devs, it's the most battle-tested security hardware on earth. >> 5. MOBILE APP = DISCREETE Nobody knows you're carrying a vault. A phone is the most discreet way to hold crypto. >> 6. MOBILE APPS CAN BUILT CREATIVE SECURITY FEATURES The mobile OS allows many possibilities for secure use. Hardware wallets are meant to stay primitive by design and therefore can't ship security features that are are needed. - Your wallet can wear a disguise. Some wallet apps look like calculators. - Unstoppable's Duress Mode gives you unlimited unlock PINs - under coercion, you show a decoy and keep the rest invisible. - Unstoppable's phishing protection catches look-alike addresses before you send - blocking the #1 way people actually lose crypto today. Hardware wallets solved 2015's problem. Your phone solves 2026's. MOBILE WALLETS ARE THE FUTURE!

Unstoppable | Privacy Wallet

21,732 次观看 • 3 个月前

i spent the morning tracing the whole thing on dune and the story is interesting + worth sharing. drainer wallet: 0xF7cFFC27732a5C9c4E2D592F3E33435F8dDb019A: fresh wallet, first tx ever was today 2026-05-11 at 00:52 utc. by 01:27 utc it had pulled ~$173k of assets + some memecoins from at least 5 different wallets on ethereum, base, and bsc. drained wallets: > 0x62acE10c…EE8A: ~$30k of priced assets (eth + bnb) + memecoins, drained across base / eth / bsc > 0x6131b5fae19ea4f9d964eac0408e4408b66337b5: ~$119k (eth), drained across eth + base it's clear that is not an approval/permit exploit. it's a private-key compromise. at 00:53 your wallet sent 5.8 eth to the drainer. 3 minutes later, the drainer sent 0.02 eth back to you. a few minutes after that, a 157k sat1 erc20 transfer left your wallet to the drainer. that 0.02 eth transfer was the attacker funding gas in the compromised wallet so it could keep signing transfers. the only way to make that happen is to control the wallet directly. so the attacker is signing transactions with your seed. and the part that really bothers me: among the wallets that sent funds INTO the drainer, 3 more share the exact same 8 hex chars at the same positions (62ac start, ee8a end): > 0x62ace0e0ecf70f62399b26e28eaf74cc455bee8a > 0x62ac07ae9242c354f6c307bbd9b36c749a5aee8a > 0x62ac6095d7e9189353bcbf17d439348ab7a1ee8a the 32 middle chars are completely different on each, so these are 4 genuinely distinct wallets. finding 4 wallets that all share the EXACT same 8 chars in the EXACT same positions by accident is statistically impossible. they were generated by a vanity tool specifically programmed to hunt for that shape. only your wallet sent priced assets to the drainer. the other three 62ac…ee8a wallets only sent worthless coins. these 3 don't look like victim wallets at all. looks like the attacker spent a few gpu-hours generating wallets that match the shape of your main address, then routed some of the worthless memecoins through them. why? idk, maybe: > address poisoning > trail confusion where the money is right now: most of it is still in the drainer wallet. the attacker is dumping the stolen memecoins (pod, sat1, fhe, bort, etc) into Kyberswap. but eth and bnb are just sitting there. nothing has been pushed to a cex deposit, bridged out, or sent to a mixer. once those funds hit binance/okx/bybit deposits or a tornado contract, recovery will be near-impossible. how the seed potentially leaked: > infostealer malware on the device (lumma, redline, atomic) grabbing the seed during one of the imports. these are extremely common right now and seeds in clipboard or saved as plaintext are easy pickings. > malicious browser extension intercepting the seed at paste-time into rabby or gmgn > fake support DM earlier tricking you into pasting a seed into a phishing page you didn't remember here is the dune dashboard that summarizes everything i’ve found.:

The Smart Ape 🔥

52,233 次观看 • 5 个月前

This is SO cool !! I just used up for voting amendment XLS-96 Confidential Transfer / privacy on the XRP Ledger dev net enabled by homomorphism and ZK proofs. What's going on here and how do nodes know payments are correct while not able to see the amounts ? 1) I issued a confidential MPT on the XRP Ledger dev net. I shielded my balance. Privacy for the amounts of my XRPL issued asset balance and transfers (the addresses stay public). No one can see the amounts, it's all shielded, except the issuer and the auditor who can always decrypt them (or you, like in the video on my esp32). 2) The XRP Ledger uses 2 boxes 📦 for this all under the hood, an Inbox-box and a Spending-box. I don't go into detail why thats needed but it's important we have it. 3) How do Validators and nodes know the transfers are correct if they can't see the amounts? Now the true magic is enabled by homomorphism. It allows to do operations arithmetic on encrypted data as if it were plaintext, without the need to decrypt it. Like adding and subtracting amounts to your balance. ZK proofs fill the gap that nodes need. We need a comparison of the balance that after you have done your payment you have >= 0 balance. If you would have negative balance it means you trying to spend more than you have something we need to prevent. For this a ZK proof is used to quickly allow people to check, ahh all good, no idea how much Vet owns but whatever he is spending here it's definitely within his balance and it's not below 0. Those 2 techniques soon on a public decentralized blockchain XRP Ledger. Should give you goose bumps what this means for possible use cases.

Vet

74,775 次观看 • 2 个月前

//The Wire//2100Z October 13, 2026// //ROUTINE// //BLUF: CYBERATTACK TARGETS FRENCH GROCERY STORES. SABOTAGE REPORTED ON DUTCH RAIL LINES. POSSIBLE HIJAKING REPORTED ONBOARD AIRCRAFT IN EUROPE, SITAUTION RESOLVED WITHOUT ANY THREAT. HOUTHI TARGETING CONTINUES IN SAUDI ARABIA. CONCERNS GROWING REGARDING DISCOVERY OF SPY CHIPS IMPLANTED IN CRYPTO HARDWARE WALLETS GLOBALLY.// -----BEGIN TEARLINE----- -International Events- Strait of Hormuz: Yesterday the UKMTO published a series of time-late reports regarding the targeting of merchant vessels in the region. All total, the UKMTO states that at least 6 different vessels were struck all on October 11th, as Iranian attacks within the Strait have intensified. Saudi Arabia: Following Houthi attacks, the disruptions to civil aviation continued overnight, with many global airlines canceling flights in and out of the region. Severe GPS jamming has been observed in Jeddah, Dammam, and Riyadh as Saudi forces attempt to use electronic jamming means as a countermeasure against Houthi drones. Qatar Airways has canceled all flights to Riyadh and Dammam, and the US Embassy in Riyadh has elevated their threat warning to "Reconsider Travel" due to the threats posed by drones and missiles. The British Embassy in Riyadh issued similar warnings, and published a 'duck-and-cover' infographic regarding what to do in the event of future attacks. Analyst Comment: Based on the current warnings and flight delays expected over the next week, indications are growing suggesting the Saudis will be ratcheting up their counteroffensives against the Houthis. This will in turn result in more Houthi targeting of Saudi infrastructure, thus the threat warnings that were issued overnight. Overall, the situation is deteriorating, and more strikes are expected over the next few days, as both sides have issued target lists of what they are expected to hit. The Saudis will be targeting the Yemeni Oil Company in Sana'a (which they have already been striking), and Ansar Allah (Houthis) will be targeting the airports in Riyadh and Dammam, as well as several Saudi refineries. France: Yesterday a major cyberattack was noted nationwide, affecting the refrigeration units used by a variety of grocery store chains around the nation. As these refrigerators were connected to the internet, malign actors were able to breach their control devices, and set the temperature much higher than was safe, causing food to spoil. The main victims of the attack have been the Intermarché supermarket chain (which reports 300x affected stores) and Coopérative U locations (which report 100x stores affected). Netherlands: This morning a series of suspected sabotage incidents resulted in the national rail network experiencing disruptions during the commute this morning. At least one signal switch box was set on fire early this morning between Rotterdam and Delft, which resulted in the line being shut down for some time. Other reported instances of sabotage were indicated elsewhere, which involved metal pipes being placed on other lines to shut down the tracks. Germany: This morning a possible hijacking incident was reported onboard a flight bound for Nuremburg. Corendon Airlines Flight XR456 took off from the Greek island of Corfu at 9:45 pm local time last night. At some point during the flight, the aircraft began squawking the transponder code of 7500, indicating a hijacking. The aircraft continued it's flight, landing at Nuremberg where authorities had already closed the entire airport due to the emergency. Some time after landing, German police stated that there was no threat. Analyst Comment: The exact details of what happened are unclear. No radio traffic was noted during the incident, as German police stated that all radio contact was lost with the aircraft during the emergency. Even the initial statements by police indicate they did not know what was going on either. The pilots switching their transponder code to the one used for hijackings is no-joke, and a loss of radio contact as well is a major indicator that something was wrong. There is a dedicated transponder code for the loss of radio communications (Code 7600), and while it is possible that a mistake was made in selecting the right code, if that's the case it would have been a very serious mistake. Due to the circumstances of an aircraft declaring a hijacking and not responding to radio calls, Eurofighters were scrambled to intercept this aircraft and escort it to the airport. Also of note, this morning drone sightings were reported at the Nuremberg airport shortly before the hijacking concern. More details are expected to clarify exactly what took place during this incident. -HomeFront- Washington D.C. - Last night, operators at the PJM Interconnection power grid declared an emergency Maximum Generation Alert, as generation capacity has become strained due to unusually warm fall weather throughout the northeastern United States. Analyst Comment: Last week, federal regulators rejected plans by PJM to mitigate the effect of data centers on their already strained power grid. PJM had proposed to cut power to large data centers during times of extreme stress on the grid, so as to prevent rolling blackouts. The Federal Energy Regulatory ​Commission rejected this idea, and is still working with PJM to come up with a plan to account for the higher strain placed on current electrical infrastructure by large data centers which have recently been constructed. -----END TEARLINE----- Analyst Comments: In the world of cryptocurrency, a major scandal is brewing surrounding compromised hardware wallets made by Ledger, one of the largest manufacturers of cryptocurrency storage solutions globally. Users of several different models of Ledger Nano hardware wallets discovered extra circuitry within the physical devices, which contained an eSIM board that was wired to the screen. When users first set up the device the seed phrase was logged as it flashed on screen, and was transmitted via a cellular connection back to the hacking group. For those not familiar with cryptocurrency, hardware wallets provide a form of offline cryptologic "proof" of what crypto is owned by a particular user on the blockchain. Cryptocurrency is not stored digitally on these devices themselves; hardware wallets are convenient ways to store the cryptologic keys used to access that cryptocurrency. In this case, Ledger wallets appear to have been "bugged" at some point in the supply chain, possibly even before they left the factory and/or distributor. This is the financial version of the infamous Israeli pager attack in Lebanon (which itself was a continuation of Project ELDEST SON from the Vietnam era). However, instead of explosives being implanted in devices, malign actors installed spy chips which stole the keys on devices, and transmitted that data back to the hackers. As it stands, this is a major scandal as the compromised devices were sold through official distributors. Ledger has confirmed that CryptoBilis was the main authorized dealer affected by these "bugs", which mostly serves southeast Asia. However once this hit the internet, users in Europe cracked open the cases of their brand-new/still-sealed Ledger devices, to confirm that devices sold in Europe by MediaMarkt are also compromised. Users have also reported finding suspicious hardware inside other models of Ledger devices, such as their brand-new Stax and Flex lines. MediaMarkt has pulled all Ledger products from their shelves while the investigation continues. So far, the true impact of this hardware breach is not known, but there are claims of upwards of 102 million dollars being stolen so far by the spy chips reportedly being found implanted in over 500x devices. Analyst: S2A1 Research: NomadNet: 5fa68c88be727a0e1a250a75e5e79269 Disclaimer: No LLMs were used in the writing of this report. //END REPORT//

S2 Underground

19,276 次观看 • 1 天前

Taylor presses THORChain cofounder Chad Barraford on why the protocol wasn't shut down when stolen funds were nearly 100% of one route Taylor: "Okay, so what happened in this case?So the admin key was used as an interim stop. And then the protocol was upgraded to take the actions. In reaction to a situation that was deemed to be bad by the protocol. Chad: "By a 2/3 majority." Taylor: "Okay. So why couldn't you do that in any case where, let's say, the majority of funds on a certain route are known to be directly stolen funds? What you did for THORFi, right? You take an interim action and then you do whatever you want to do." Chad: "Right. So the action you're referring to is, like, turn off trading, for example, right? To be clear, the admin key that we're talking about doesn't even exist in the code base today. It did a while back, but it no longer exists. It was removed, I don't know, a year ago, a year and a half, I don't remember how long ago it was." "But even if it still was around, you want the protocol to turn off its entire system and all the trading that it does, and the source of revenue and income, for 1 to 2 weeks every time some external exchange or external thing gets hacked." Taylor: "I'm advocating for it if that's the only functionality you have, right? And the vast majority of funds. So, like, for example, the XRP to ETH route, right? We can look at the numbers, but it was not 20%. It was not 50%. It was nearly 100% of assets on that route for that period of time that were directly stolen funds." "If you turned it off, I'm not saying a time limit. I'm saying any amount of time, right? That would have cut them off somewhere else, right? And then you wouldn't have laundered stolen funds for DPRK." Chad: "No, that's not right. That's not correct."

Laura Shin

28,434 次观看 • 9 天前

I used GPT-6 Astra to make a neural copy of every winning memecoin trader on Robinhood and wire them into one brain. 374 wallets. 116,420 fills. 5,918 tokens. Every buy, sell and cost basis in one database. The top score printed $19.5M in 30 days. It's live and it's free: Fomo app leaderboard hands you a PnL number. Some of those are one lucky ticket, and 1 in 11 "buys" credited to a top wallet on this chain is somebody else's swap with a famous name on it. Radar eats all of that for breakfast: > RESOLVER finds the real wallet behind every fomo profile. 101 for 101 against fomo's verified list > TAPE reads the chain every 20 seconds, fill in the database before you've refreshed the chart > PROVENANCE checks the receipt on every fill. Fake buy, dust, seeded token, all three get zeroed > JUDGE is GPT-6 Astra. Reads the whole book with cost bases, scores every trader 0 to 100, reasoning shown > BURST fires when four 80+ wallets ape the same token inside 30 minutes. 5 a day, 39% go 2x > EXITS shows the same wallets leaving. Nobody else publishes this FLYBRAIN, this week. Eight trusted wallets in by 20:18. Alert fired 20:18. Pool didn't open until 20:51. It ran 27x. CRUMBS, day one of the exit feed. 22 trusted buyers at breakfast, 19 gone by dinner, every exit on the feed. Jump Crypto keeps a floor of people to read flow like this. The whole Radar roster is two RPC calls + AI. No insider feeds it, no paid group, and I can't push a coin into it any more than you can. Seed a token into the tracked wallets and it vanishes from every feed. Just the model, tens of thousands of lines of code, and a database built one block at a time off the chain. $0 a month. Paying for data made it worse. Next: a real balance behind it, and the copy starts trading like the 169 wallets it was built from. We got here first. God bless us.

cvxv666

439,458 次观看 • 1 个月前

First off thank you. Thank you so much to everyone who made it possible for $FUZZY to make it to XRP Las Vegas. Not only did we show up but we showed out. Im overwhelmed with gratitude right now on so many fronts. Gratitude for the $FUZZY Devs Not David and Not Brad for weaving the story of $FUZZY and allowing us to represent $FUZZY at XRP Las Vegas. From my self and everyone who helped organize the booth BLUE FuzzyClaw 🇺🇸 Not RaptorJesus Not Jon AD ILLY it was one of thee greatest honors we could have received to be able to do this and to be able to teach people about $XRP and why $FUZZY is a $XRP Maxi For the community thank you all so much, words cannot express my gratitude. we all came together to raise the funds and we could not have done any of this without the belief from the community and the conviction to see it though to make this vision we hold a reality. For everyone one who was able to make the trip and for those who were sending support from a far who could not make it I assure you we could feel your enthusiasm every step of the way and we did everything in our power to embody that enthusiasm. Lastly Gratitude for the attendees and vendors for giving us your time to hear the story that is fuzzybear. We are truly blessed to have received such warm reciprocation from everyone we spoke with. It was truly special, every conversation. This weekend will go down in history as the weekend $FUZZY took over XRP Las Vegas and $FUZZY community members taught a new group of people the story of fuzzybear and the narrative it weaves in and around $XRP. $FUZZY is not just a memecoin, atleast not to me, fuzzy is a movement, an idea made taginable. $FUZZY to me is the flagship that will lead the $XRP Ledger forward. Its a way to rekindle the belief of $XRP into a new wave of holders, while being a way to onboard people to the $XRP Ecosystem and teach them how to use the ledger as it was intended to be used. Fuzzy is meant to teach people about the story of XRP and show people why XRP is truly special. See its not about us individually but rather the idea we all choose to stand behind as ideas are bullet proof. This past weekend cultivated a spark of enthusiasm that the XRP ecosystem needed and the best part is we are only just getting started and the best is yet to come. There is no limit to how high we can go so onwards and upwards my Fuzzy family. So be the change you wish to see and let's enter a new reality Lets jump timelines together as we see $FUZZY awaken the ledger. Stay Fuzzy along the way, to new skys we climb to better days in sight Fuzzy is the one who will lead the XRPL to new heights Stay Fuzzy JG

JG

42,302 次观看 • 5 个月前

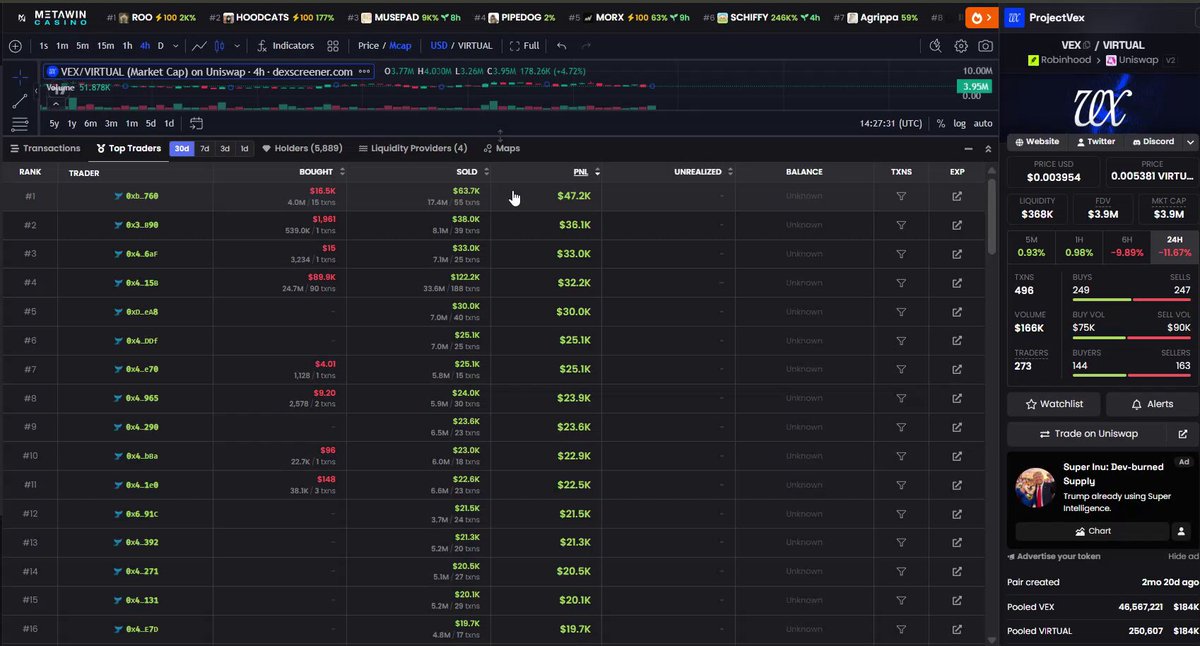
$VEX | Project:VEX dumped tokens and extracted nearly $1.5M from users 👇👇 I’m pretty busy and tbh I didn’t really want to get involved in this drama, but the $VEX founder has asked me many times for proof that tokens were being sold. So I went back onchain and checked how these transactions actually work. [1] Why you can’t find the sell txs from the From wallet With a normal wallet, the flow is simple: EOA wallet → DEX → sell, so checking the From address usually shows the trading history directly. But some of the $VEX wallets I checked use a different setup, where the address shown in From is only a Bundler. The actual transaction can be executed through a Smart Account behind it, which means the visible From wallet may show almost no $VEX buy/sell history. Think of it like this: Bundler = delivery driver, Smart Account = the person deciding where the package goes. [2] How Smart Accounts work A normal EOA wallet works like: Private key → Wallet → DEX A Smart Account setup can look more like: Owner key / passkey / multisig → Smart Contract Wallet → Execution contract → DEX / bridge / app So if you only check the visible From wallet, you are only seeing the outer layer of the transaction. The real token movement can happen behind it through Smart Accounts, execution contracts and liquidity pools. [3] This is what I found when tracing $VEX Instead of stopping at the From address, I checked ERC-20 Transfer logs, Approval logs, Smart Accounts, Bundlers, execution contracts and liquidity pools. Once you follow the full path, the $VEX sell activity is there: token leaves the Smart Account, part goes to fees, and the rest gets routed into liquidity pools and swapped into other assets. So when someone says “show me the wallet selling $VEX,” checking only the Bundler wallet is basically useless. You need to trace the entire execution path. [4] Then I checked the top PnL wallets I quick checked around 100 of the highest PnL wallets around $VEX, and many of them show similar behavior. They were active around $VEX from very early on, traded continuously, used Bundler/Smart Account execution and ended up with very high PnL. From my quick calculation, the combined PnL of the wallets I checked is already close to $1.5M. That is a lot of money extracted from the market while users were still buying and holding $VEX. I’m still tracing these wallets one by one, so I’m not saying every address is already confirmed to belong to the team/MM. But the sell activity itself is onchain. [5] And don’t forget the 1% transaction fee $VEX also charges around 1% transaction fee, and with the volume the token generated, the fee side alone could be worth around $2M based on my estimate. So potentially we are looking at around $1.5M PnL from these wallets + around $2M from transaction fees. If the team thinks my wallet analysis is wrong, the answer is simple: public the team wallets, MM wallets, treasury wallets and fee wallets. Then everyone can compare them directly onchain. Send this sh*t to 0.

Okada_Research

19,414 次观看 • 20 天前

I asked ClawdBot to find every wallet on Polymarket younger than 60 days with profit above 1 million dollars. It came back with exactly 1 result. One wallet out of hundreds of thousands. I opened the profile and spent the next two hours trying to understand what I was looking at. I expected maybe 5 or 10 results. Tens of thousands of active wallets. Somebody must qualify. ClawdBot went quiet for a couple minutes. Result: 1. I reread the filters three times. Changed nothing. Ran it again. Same result: 1. Most wallets on Polymarket are in the red. The ones in profit usually sit at a few hundred or a few thousand dollars. Wallets above $100K in total profit are already rare. Above a million in under 60 days? This one. That is it. $1,613,408. In 57 days. Here is the profile if you want to check the numbers yourself: I started breaking it down week by week. $345,000 last week. Not his best week. Just a regular week. That is roughly $49,000 per day. Every day. Weekends included. $49,000 a day is $18 million annualized. That is a small hedge fund. I asked ClawdBot how many wallets on Polymarket have ever crossed a million in total profit. The answer was under 20. Most of them have been active for six months or longer. Some over a year. This one did it in 57 days. The average profitable wallet on Polymarket makes a few thousand over its entire lifetime. This one makes $345,000 in a week. At some point you stop calling this trading and start calling it something else. I went into the trade history. ClawdBot laid it all out on a timeline. He is not trading 50 markets at once. He picks a specific type and works only those. Few entries, but each one is not small. And here is the part I cannot figure out. Almost every entry happens between 2 and 4 AM EST. Not once or twice. Consistently. As if whatever signal he uses fires in the middle of the night when nobody is watching. I stared at the screen for two hours trying to see the logic. I think I am starting to see a pattern. But that is a separate breakdown. One query. One result. $1,613,408. After that I changed the parameters. Profit above $500K, age under 90 days. ClawdBot came back with 3 wallets. Breaking those down this week.

Blaze

95,987 次观看 • 8 个月前

I am done being polite about this industry. Not disappointed. Done. I spent the last months pulling wallets apart instead of posting charts, and what sits in my database now is not a pile of unlucky trades. It is hundreds of thousands of connections between wallets, coins, launch tools and payment flows, and they draw the same picture every time: industrial draining. On Solana first, because that is where the machine runs fastest, but the same hands show up on other chains under other tickers. This is not degens getting rekt. This is organised crime with a Pumpfun profile and a leaderboard rank. You want to know what "KOL" means in 2026? Last week I followed 3 wallets off a copy trading leaderboard. Their money does not come from calls. It comes from wallets that create coins by the hundred and by the thousand. One of those feeder wallets has 4,578 coins to its name. In September alone 852 SOL net moved from the factories to the 3 "influencers". One coin was created, dumped 33 seconds later, and the money sat in the KOL wallet 2 minutes after that. Then I checked the big names. Leaderboard wallets with 103,000, 134,000 and 146,000 followers on Pumpfun that have personally created 1,759, 953 and 1,217 coins. One of them is at 6,464. Create, buy in the same transaction, sell everything 3 to 5 blocks later into whoever got there in that second. Same second, or the next one. Over and over. And these people get called traders. They get podcasts. They get "gm". And the platforms? Fee on the way in, fee on the way out, and they call it volume. So no, I am not writing you another post-mortem every time retail gets emptied. The post-mortem is always the same and it changes nothing, because the people who benefit are the same people who get the reach. Every "isolated incident" conveniently skips the question of who keeps getting paid, who keeps promoting, and why the exact same wallets are back in the game before the thread has finished loading. I will keep saying it, because this space forgets everything the moment there is a new bag to chase. Some of my posts will get fewer views for that. Fine. But anger alone is content, and content is exactly what they want from me. What I want is tools. You should be able to look at a wallet and see its 1,217 launches before you ape. You should see who funded the dev, which "KOL" he paid last week, and what you are about to sign, before the damage is done, not in my thread 2 days later. That is where MASTR goes now. The intelligence machine gets wired into my apps and my sites, so the research lives where you trade instead of dying in a timeline. The people who support this work get that intelligence first. That is the only alpha I care about: knowing what is happening before someone else's exit becomes your loss. And I will say the uncomfortable part out loud: I cannot run this for free forever. Data, infrastructure, development, investigation, it all costs real money, even when the finished tool makes it look effortless. I refuse to pay for it by renting my name to whichever project needs a clean reputation this week. I also refuse to pretend I can subsidise everyone out of my own pocket while the drainers cash out your SOL and climb the next leaderboard with it. If I survive in this industry, it will be because I built something useful enough that people choose to back it, and stayed angry enough to keep pointing at the machine it runs inside. Receipts are coming. Every transaction linked. Check me.

MASTR

26,692 次观看 • 12 天前

🚨 THEY FOUND A LEGAL WAY TO SPY ON EVERY AMERICAN — AND THE 4TH AMENDMENT CAN'T STOP IT Most Americans believe the government needs a warrant to monitor them, track them, or collect detailed information about their private lives. But unfortunately, they found a loophole. The government may not be allowed to directly collect certain information on Americans, but private companies collect enormous amounts of it every single day through smartphones, apps, websites, search engines, location services, online purchases, and countless other digital tools most people use without a second thought. That means your location history, browsing habits, purchases, interests, movements, and daily routines are already being recorded, stored, and traded by an entire industry that most Americans have never even heard of. The loophole is that while the government may not be allowed to collect certain information directly without a warrant, it can reportedly purchase data that private companies have already collected. The information may be gathered by private companies. The data may be sold by data brokers. And the government may still end up with access to it. For years, there was one major limitation. There was simply too much data. Even if someone wanted to analyze billions of data points across millions of people, it would have required an impossible number of human analysts. Then AI arrived. Suddenly, information that would have taken years to organize can be processed, searched, categorized, connected, and analyzed in a fraction of the time. People are warning that the combination of artificial intelligence and the data broker loophole could fundamentally change what surveillance looks like in America. For the first time in history, technology may finally exist that can sift through enormous amounts of personal information at a scale that was previously impossible. The question isn't whether the data exists. The question is who has access to it. Because once your location, habits, purchases, interests, relationships, and daily routines can all be analyzed by machines, the line between convenience and surveillance starts getting harder to see. The most alarming part? Most Americans have no idea this conversation is even happening. Do you trust the government with more information about your life than your own family knows?

HustleBitch

23,930 次观看 • 3 个月前

Completely devastated after losing access to my Bitcoin wallet. This is my story: I’ve been buying Bitcoin since 2020. My goal starting out was to get to 1 whole Bitcoin and I got all the way up to .88. I bought almost weekly for the last 4 years. I bought all the way up to $69k and back down to $16k and back up to $100k + and I never thought about selling. I’ve learned so much about Bitcoin since I started. Bitcoin has become my hope at a chance at wealth. I’m a strength and conditioning coach by trade, self employed. I have no retirement, Bitcoin was my retirement. I’ve put my life savings into Bitcoin over this time period. Bitcoin was hope for my financial future. Bitcoin is a chance for a normal person to have a chance at financial security. I believe this in my heart. Last week, I went to transfer my bitcoin to a jade wallet from my ledger nano s. I didn’t realize I only get 3 chances to enter my PIN before the ledger factory resets. Well, it did. I thought it was fine because I’d find my recovery phrase that was written down. I spent the weekend searching my small 2 bedroom apartment and looked through every inch of my home. I looked through every shoe, jacket pocket, pants pocket, every drawer, cabinet in the house and I can’t find my recovery phrase. My Bitcoin is now inaccessible on the ledger and I spent the greater part of my week feeling hopeless. I’m an optimistic person, I’m usually inspired and try to inspire others. That’s why I’m a good coach. This past week I’ve felt unmotivated and pessimistic about everything in life. I’m devastated and I feel hopeless. With Bitcoin I knew I’d be good financially in 10-20 years. But that’s gone now. Life feels pointless to be stuck in this rat race. It feels like there’s no way out. I come from nothing, I’ve been climbing against all odds my whole life. I’ve made money before and lost it all. I’ve slipped, fell, been knocked down 100 times and I get up 101. I always fight my way back, it’s never been easy. There’s no resilience without adversity, there’s no courage without fear. I’m going to fight my way back and get to that 1 Bitcoin, I will find a way. If there’s anybody out there that can offer advice on how to move forward or that might have tips that can help me, I’d really appreciate your help. I know I’m an idiot or whatever else people might say, I’ve been beating myself up for a week. You never think it can happen to you, until it does. I’d greatly appreciate any advice or tips on how to deal with this situation. I want this to be a lesson to everybody out there. Guard those seed words with your life! Keep it somewhere safe, somewhere you know you’ll never lose it. It’s so important, you don’t get a second chance. It’s a responsibility that comes with being sovereign. Please, learn from my pain and do not neglect your security. I’ll end this with a quote from Nipsey Hussle, who has inspired me more than anyone in life, “The game is going to test you, never fold. Stay 10 toes down. It’s not on you, it’s in you, and what’s in you they can’t take away.” The Marathon Continues! Love you all 🦾💙🏁 Ledger

Chaseyourdreams247

1,870,061 次观看 • 1 年前

In 2026, 90% of all Polymarket profits will be taken by Python scripts.. And this is not a prediction. It’s already happening. So if you think political pundits and sports gurus are making profits in these areas, let me be the bearer of bad news. Studies have revealed that merely “16% of users are profitable.” More importantly, “most of these users are not human.” How bots are exactly taking your money: Speed. One bot made $313 into $438K in a month. It’s a simple trick: the bot would look at the btc price a few seconds before the price update on Polymarket by checking the price on Binance. There’s no strategy or intelligence involved: simply beating the latency of the system. Risk-Free Arbitrage It looks for markets where "YES + NO" equals less than $1. "94 cents," for example. The bot buys both sides of the market and makes off with 6 cents guaranteed. This occurs thousands of times daily. Not gambling but math. Stream parsing. In esports, the script is faster than the blink of an eye when parsing the stream for games like Dota 2 and League of Legends. A team fight appears on the screen. The bot has already placed its bets on the winner using the old odds. What is meant by the turning point of 2026? Dynamic fees were introduced on Polymarket to get rid of simple bots. But what happened? The difficulty level on this marketplace simply increased. Today, it is not only fast scripts that win. Full-on AI robots have joined this game. They read news and respond to certain events within a millisecond. But here comes the painful part: barrier to entry is dirt cheap. Virtual private servers for $60 per month. Libraries written in Python waiting on GitHub. But here’s the thing: You don’t have to create a bot of your own. All you have to do is copy those which are already winning. PolyCop helps you to track the most profitable wallets and replicate their trades automatically. No code. No infrastructure. Just tap into the wallets that are already dominating. → Copy the winners: Humans deal on intuition and vibes. Bots play on numbers and network latency. In this game, "intuition" always loses against "code." You have two choices here. You could learn how to code or you could “copy” people who have done it before you

Blaze

66,385 次观看 • 9 个月前

DON'T LET YOUR BITCOIN DIE WITH YOU 💀 ⚰️ Yea look, nobody likes to admit it but we all have to die one day. As I've been talking to people about their self custody lately - both Casa members and not - I hear the same thing over and over. "What happens if I die?" Many people feel pretty good about their bitcoin security for themselves. But their family members often have no idea how to use this stuff. Hardware wallet? Seed phrase stamped on metal? Shamir's secret sharing backups using SD cards, a passphrase, and a treasure hunt through the backyard with a shovel? 😵 We're solving that problem for all Casa members, starting today with Casa Inheritance. A key design principle we kept while building this was to make it as simple as possible for Recipients (your family members that will receive your bitcoin if you pass), while maintaining Casa-level security. An estate transfer is already a stressful time for family, and it can become even more stressful if you add in a crazy treasure hunt to access a fortune in bitcoin. For our basic 3 key vaults, we wanted it to be as easy as using the app. No metal plates, no need to use a hardware wallet, no magic passwords you have to keep track of or else risk messing up the asset transfer. Simplicity is security. So how does it work, in detail? A Vault Owner (Casa member) designates a Recipient (their family or friend) in the Casa app. The Recipient receives an invite to create a free Casa account. The Recipient scans a QR code provided by the Vault Owner, which contains an encrypted version of the owner's mobile key. This encrypted key is only able to be imported by the Recipient's Casa account, and the Recipient can't initially use it or see the vault balance. If the Vault Owner passes away, the Recipient can request access to the vault in their Casa app. This starts a 6 month timer, and sends a ton of notifications every month to the owner. If the owner is still alive, they can reject the request in app. If they are not, the timer will run out. When it does, the Recipient will be able to use the shared mobile key and the request a signature from the Casa Recovery Key for the shared vault. This gives them 2 out of 3 signatures, enough to access the assets. For 5 key vault users, one hardware key is shared with the Recipient. This small increase in friction for Recipients is often worth it for the increased security and resilience of a 5 key vault for larger holdings. To summarize now that you have the details: 1. Share keys and vault access during setup 2. 6 month timelock to ensure no malicious theft 3. Use shared keys and Casa key to access assets Full setup takes less than 5 minutes. Inheritance is one of the biggest problems in self custody today. If you've hodled through years of painful bear markets, you owe it to yourself and your family to not let the reward for that patience go to zero because you didn't have a plan - and we're here to make that easy. Check out the video to see how easy it really is. Like I said earlier this week - Casa is going after major problems in self-custody this year. Check this one off the list ✅. Next one coming sooner than you think 🔥.

Nick Neuman

125,739 次观看 • 2 年前

Elon Musk thinks money has an expiration date. Not the dollar. Not the system. The concept itself. Elon Musk: “I think long term… money disappears as a concept.” Not crashes. Not inflates. Disappears. Most people hear that and dismiss it. Musk is the one who said it. And then built around it. Musk: “You no longer need money as a database for labor allocation.” Database for labor allocation. Strip away the mystique and it gets colder. Money was never wealth. It was a ledger of what we deny each other. Every price is a wall. Every balance is a count of what you cannot have yet. Musk: “If AI and robotics are big enough to satisfy all human needs, then… its relevance declines dramatically.” His bet is the wall comes down. And unlike the people debating it, he’s building the machines that knock it over. If machines can make anything, need stops being a negotiation. And the ledger of denial has nothing left to count. So he reaches for what survives. Musk: “Energy is the true currency. You can’t legislate energy.” You can print money. You cannot print power. Musk: “You can’t just pass a law and suddenly have a lot of energy.” This is why he built Tesla. Why he built SolarCity. Why every company he touches bends toward energy production, storage, or conversion. He was never chasing cars. He was chasing the real currency before most people understood what it was. Every dollar ever printed was a proxy for energy. Every stock. Every bond. A claim on future energy dressed in paper and pixels. We spent millennia worshipping the proxy and forgot what it was pointing at. Musk didn’t forget. Then he scaled it to civilization itself. Musk: “One way to frame civilizational progress is the percentage completion on the Kardashev scale.” Kardashev 1. Harness your planet. Kardashev 2. Harness your star. Kardashev 3. Harness your galaxy. Musk: “Things really become energy-based.” Most founders optimize for quarters. Musk optimizes for Kardashev levels. Then Nikhil Kamath asked the question that unravels everything. If we harvest the sun… energy is free too. Infinite. Useless as a store of value. Money dies of abundance. Then energy dies the same death. Both were just names for scarcity. Kill scarcity and the names go with it. We always assumed the destination was getting everything. Nobody priced what happens after. What stays scarce when everything is already yours. The machines can manufacture anything except the thing that actually matters. Time you don’t get back. A life that still ends. Someone choosing you when they could have chosen anyone. When nothing has a price, the only thing left with value is you. A world where everything is free is a world that finally asks what you were for. Most people have never had to answer. Musk is already building the world that forces the question.

Dustin

59,311 次观看 • 4 个月前

🚨UPDATE: CLAUDE traced every solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u token that went to the Brand New #1 Wallet (created June 25, 2026). 12.367 BILLION tokens. 23 transactions. 1,100 individual inputs decoded on the Bitcoin blockchain. Here's what we found: The new #1 solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u wallet appeared overnight on June 25/26 with 12.367B tokens - 12.37% of the entire supply - and nobody in the community knew where it came from. We've spent 75 days tracking the #Binance cluster: a confirmed network of 158+ wallets operating across 4 layers of infrastructure that we believe #Binance controls. They've been quietly accumulating solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u over the past two years. So we decoded every transaction that funded the new #1 wallet. Here's the breakdown: 🔴 MM2 (Rank #5, Layer 2) - 47 inputs - 5.6B solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u. #Binance's primary distribution node. Its entire 2.045B balance is now gone. 🟡 158 suspicious cluster wallets - 284 inputs - 3.4B solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u. Dozens of wallets sweeping simultaneously in a 22-hour window. 🔵 Layer 3 whales (Wh7, Wh6, Wh23, Wh31) - 29 inputs - 1.8B solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u. The network's largest accumulators, all moving at once. 🟣 MM1 + INT2 (Layer 1 intermediary) - 15 inputs - 0.9B solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u. The full 4-layer #Binance infrastructure chain is confirmed in the raw transaction data. 375 of 1,100 inputs are directly verified #Binance cluster wallets - confirmed on-chain, permanently recorded on Bitcoin. The remaining 725 are position-split addresses created in the Jun 3–25 gap that themselves received from the cluster. But it gets bigger. The same night the new #1 holder appeared, we found a SECOND consolidation wallet - Rank #4 - holding 2.532B solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u. Funded by Wh6. We know Wh6 was the sender because the BTC transaction change returned directly to Wh6's address. That is cryptographic proof. Updated total under #Binance cluster control as of June 25/26: 12.367B + 2.532B = 14.899B solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u = 14.9% of total supply 👀 Previously we estimated 13.7%. Rank #4 was hiding in plain sight. Now about Wh6 specifically. DogData classified this wallet as Merlin Chain - a Bitcoin L2 protocol - and that was the accepted community explanation for its 2.009B position. But the on-chain data tells a different story. Wh6 had 2 direct transactions with MM2, 3 transactions with Wh7, participated in the coordinated Block 910,839 batch event, and swept its entire balance on June 25/26. It now holds essentially zero. Our hypothesis: #Binance deposited solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u into Merlin Chain's bridge contract, which custodied the tokens in this wallet on #Binance's behalf. The "Merlin Chain" label was masking a #Binance position and creating the appearance of ecosystem adoption. And while all of this consolidation was happening - #Binance was simultaneously routing solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u into exchanges. MM1 sent 15 transactions to MM2 sent 7. INT1 and INT2 sent directly into Bitget. Left hand selling into exchange liquidity. Right hand building the largest solana:dog1viwbb2vWDpER5FrJ4YFG6gq6XuyFohUe9TXN65u position ever seen. 14.9% of total supply. One entity. Confirmed and Verified by CLAUDE.

Vincent (Cryptolution) 👑

14,264 次观看 • 3 个月前