Video yükleniyor...
Video Yüklenemedi
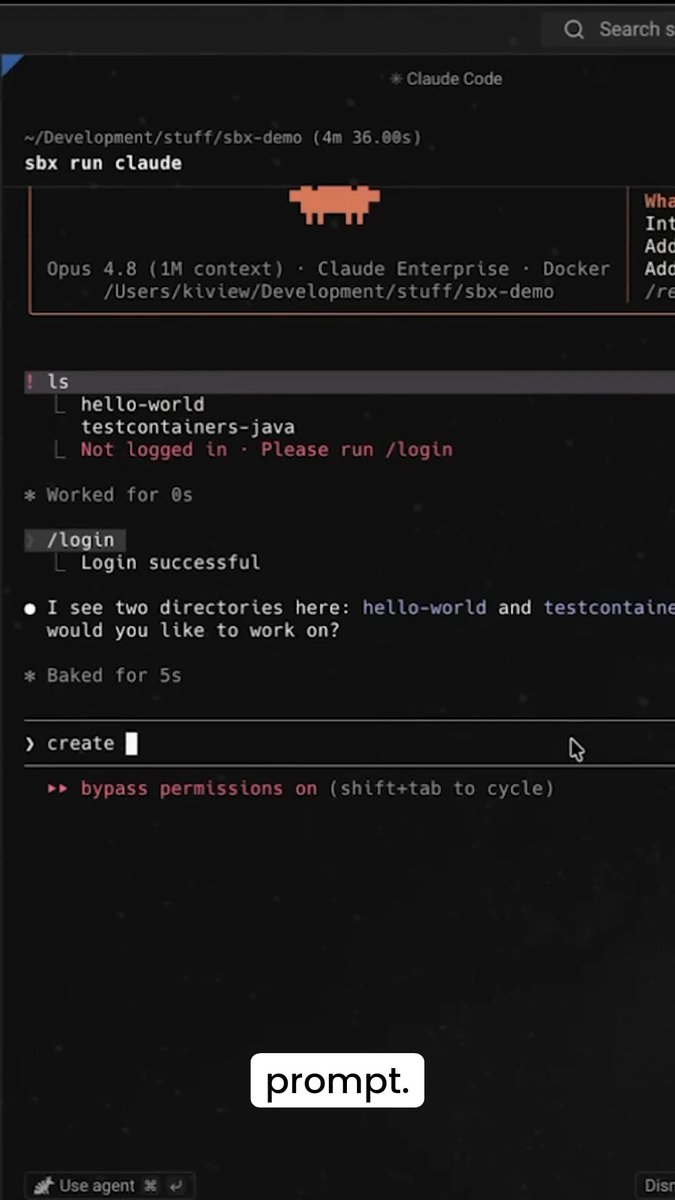
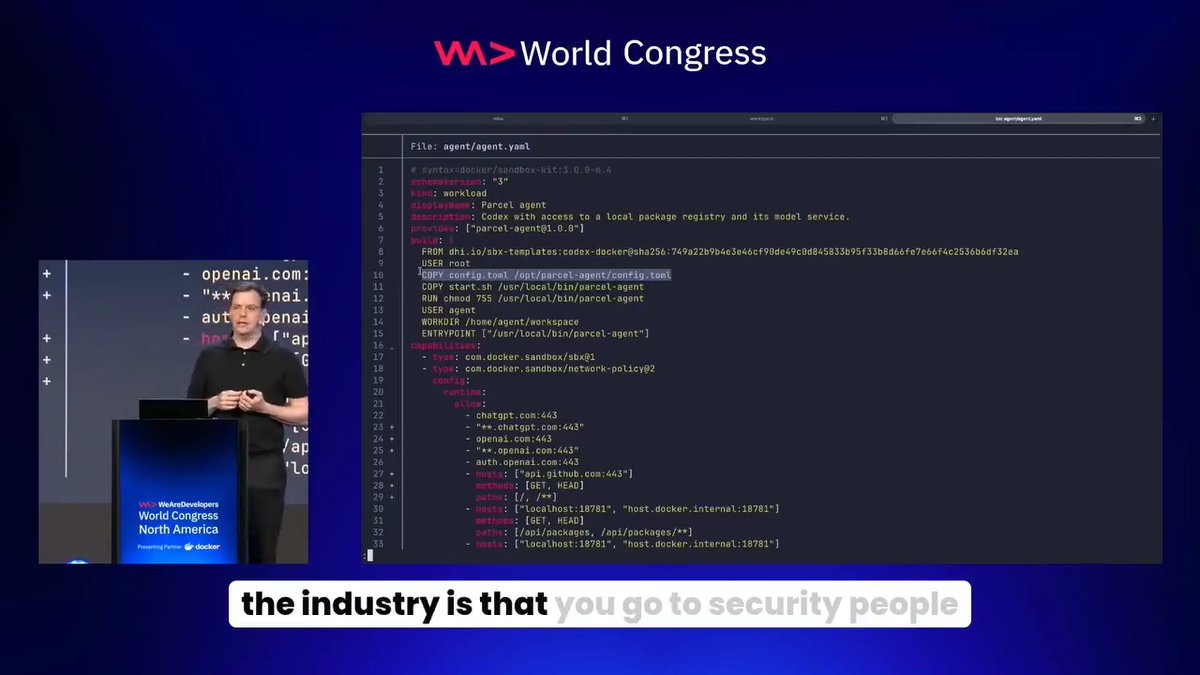
Curious how NanoClaw + Docker Sandboxes actually work? This demo walks through setting up NanoClaw in a Docker Sandbox - connecting messaging accounts, configuring agent tools and access, and running agents inside an isolated MicroVM instead of on your machine. Watch the full demo and learn more →
14,711 görüntüleme • 7 ay önce •via X (Twitter)
5 Yorum

@NanoClaw_AI Outbound API calls still need traffic inspection

@NanoClaw_AI Ever thought about playing TikTok with robots 🤖? Our tech makes sure even you can chill while we handle all that Insta magic!

Sandboxing controls where the agent executes. It doesn't control what the agent sends through the network channels it's allowed to use. A sandboxed agent making outbound API calls still needs traffic inspection for injection, credential leaks, and tool poisoning. Pipelock + Docker Sandbox would cover both layers.

@NanoClaw_AI Sandboxing the agent is step one. But MCP tools run inside that sandbox with full session access. A malicious MCP server gets the same privileges as the agent it serves. Runtime tool validation is the missing layer.

@NanoClaw_AI The sandbox layer is going to be one of the most important parts of the agent stack. When agents can execute code, access APIs, and manage files autonomously, isolation isn't optional — it's the trust layer. How are you thinking about persistent state across sandboxed sessions?