Loading video...
Video Failed to Load
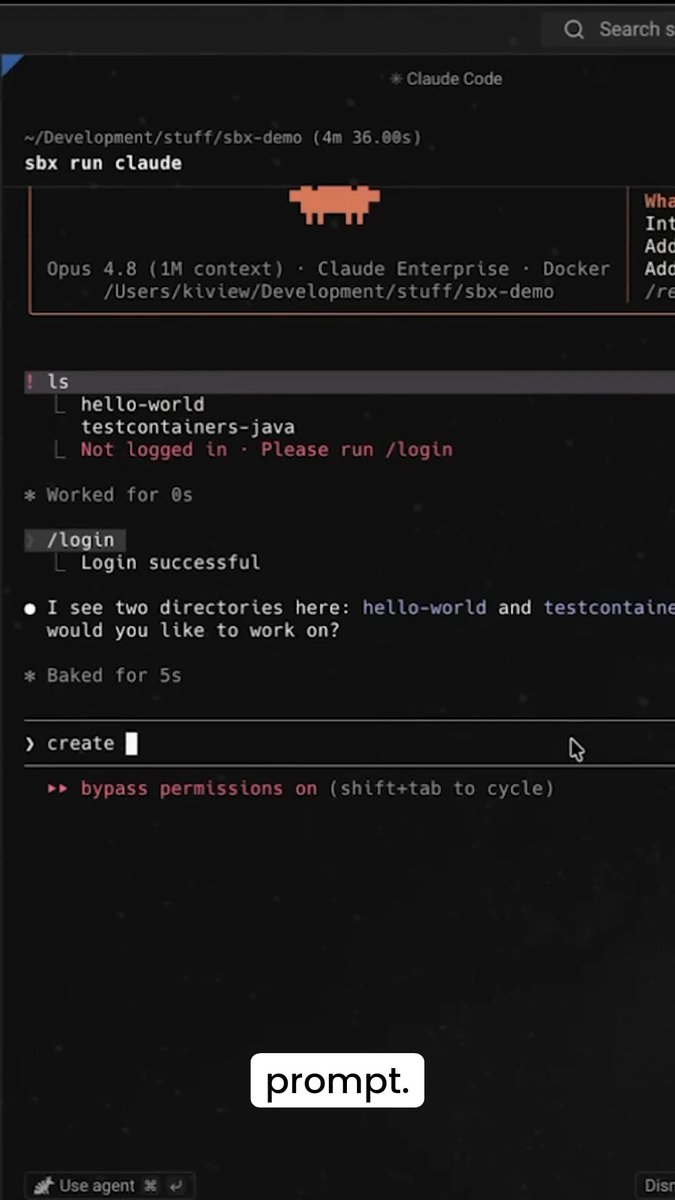
At WeAreDevelopers, Docker CISO Mark Lechner highlighted how most orgs have no visibility into what their agents can reach. His take: manage manifests as code, only run agents in observable environments. Cloud Sandboxes is the boundary that stays with your agent, even after you close your laptop. Try it... show more
18,205 views • 1 month ago •via X (Twitter)
7 Comments

@WeAreDevs The manifest-as-code framing is the useful part: the agent boundary should travel with the run, not the laptop. I'd want every sandbox receipt to include tool allowlist, network egress policy, secret mounts, and expiry so reviews can diff behavior, not trust posture.

@WeAreDevs Such an interesting seminar

@WeAreDevs Agent permissions are only useful if you can inspect what the agent actually reached and did. “Allowed” without observability is still a pretty weak safety boundary.

@WeAreDevs we diff the container mount before accepting an artifact. one Docker run wrote into /tmp, then claimed the workspace was clean. do you expose the final mount diff in the sandbox logs?

@WeAreDevs agent boundaries leak like sieve without sandboxing

@WeAreDevs ファーストビューがすべてじゃない理由 「観測可能な環境」はセキュリティのデフォルト設定みたいなもの 脳は透明なルールがあると安心して動ける構造 まるでガラスの橋が渡りやすいのと同じですよね

@WeAreDevs managing manifests as code makes the boundary actually stick