正在加载视频...
视频加载失败
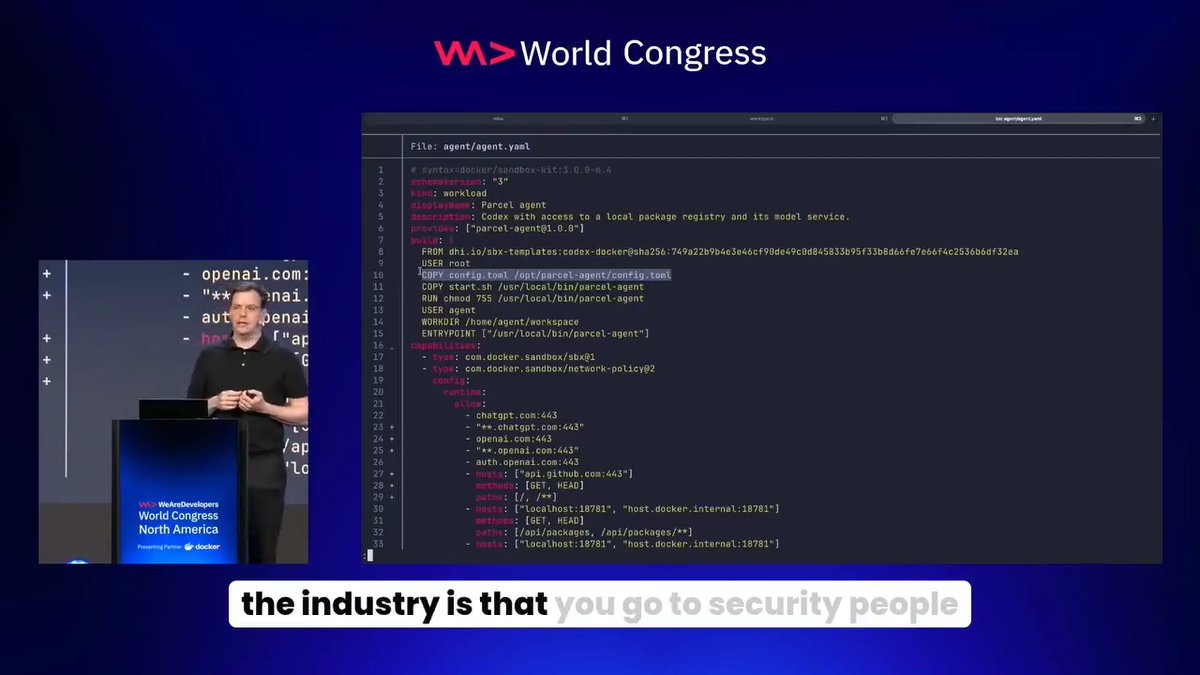
“Don't trust a model to govern a model." Mark Cavage's keynote at WeAreDevelopers covered: - New Cloud Sandbox offering - Sandbox Kit Spec, a common foundation for the agent ecosystem - Surprise guest Hervé Bizira from Nous Research Trust comes from the system around the agent. Watch:
17,388 次观看 • 9 天前 •via X (Twitter)
7 条评论

@WeAreDevs @NousResearch sandboxing and shared specs make system-level trust much more auditable

"Trust the system around the agent, not just the model" is the right framing. Sandboxes are useless if the agent still gets a live prod database URL by default. The Sandbox Kit idea only works if env isolation and network rules are boringly consistent across local and cloud. Curious whether the spec covers egress allowlists and secret injection, or if that's still left to each runtime.

@WeAreDevs @NousResearch Agent 治理应落在模型之外:默认无网络、只读挂载、短期凭证、CPU/内存/时限配额、系统调用审计和可销毁环境;策略由内核与平台强制,模型只负责提出动作而不能修改护栏。

@WeAreDevs @NousResearch Exactly. Isolation is necessary, but the operating model matters just as much: declared capabilities, scoped credentials, egress policy, and an auditable event trail. A sandbox without those signals contains damage better than it explains authority.

@WeAreDevs @NousResearch The hard part is what 'dumb' means when the sandbox has to parse agent outputs to enforce policy. Any parser is attack surface.

@WeAreDevs @NousResearch 'don't trust a model to govern a model' is the whole agent security story. the sandbox boundary has to be dumb, deterministic and outside the thing it contains

@WeAreDevs @NousResearch 这句说到点子上了