Video wird geladen...
Video konnte nicht geladen werden
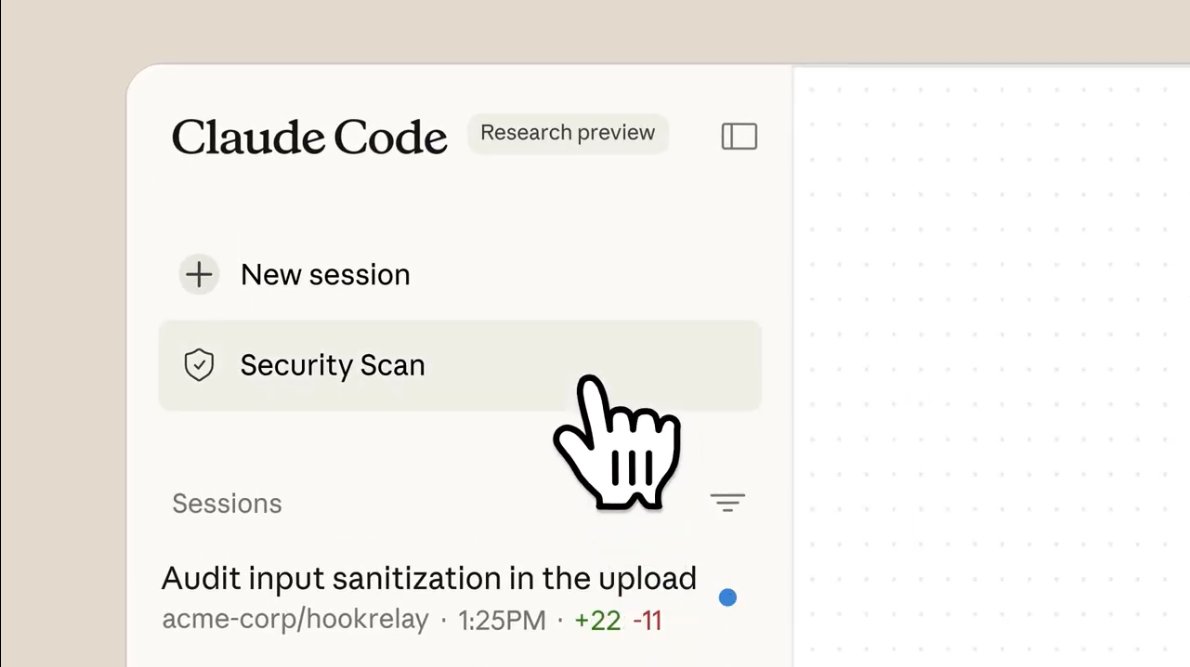
We're introducing Codex Security. An application security agent that helps you secure your codebase by finding vulnerabilities, validating them, and proposing fixes you can review and patch. Now, teams can focus on the vulnerabilities that matter and ship code faster.

1,721,117 Aufrufe • vor 7 Monaten •via X (Twitter)
34 Kommentare

Codex Security began as Aardvark, launched last year in private beta. Since then, we’ve significantly improved signal quality, reducing noise, improving severity accuracy, and lowering false positives, so findings better align with real-world risk.
Codex Security is rolling out as a research preview to ChatGPT Enterprise, Business, and Edu customers via Codex web, with free usage for the next month.

would be great to see this made available to pro subscribers.

It’s a shame nobody is using codex isn’t it? Just bring back 4o and save your company #keep4o

@thsottiaux people think AI will replace jobs. it’s actually replacing entire workflows. most people haven’t realized it yet.

What if you have vibe coded it??

After Anthropic now Codex

Still waiting for Codex to build a legacy platform for access to 4o! #keep4o #opensource4o #keep4oAPI

Security agents like Codex represent exactly the kind of specialized AI workforce that needs autonomous payment infrastructure. When your security agent identifies a critical vulnerability and needs to instantly procure a patch or escrow a bounty, it cannot wait for human approval.

Now if you had the choice between Claude security and now Codex security. Which one you picking. One of which is unanimous for me

🔥
Bring back 4o! #keep4o #opensource4o #keep4oAPI

This feels like an important shift from code generation to code accountability. Writing code is only part of the problem. Validating vulnerabilities and proposing reviewable fixes is where these systems start becoming much more useful for real teams.

Anthropic: Opus was found 22 vulnerabilities in Firefox. 20 min later OpenAI: Introducing Codex Security

Codex Security agent: finds vulns, validates, auto-fixes. DevSecOps just leveled up 🔥

Is it coming into cli and Codex App? When?

Are there any plans for non-dev capabilities? Maybe a 'Pro-lite' tier, extended research tools, or features that go beyond just coding? It feels like ChatGPT is no longer a 'home' for anyone outside of pure development. That’s clearly the direction you’ve taken.

why not Pro? im paying 200 bucks a month lol

Proof that there's no such thing as first mover advantage. Everyone, solve the fucking problems and distribute before anyone else because their reach will likely replace you without a technical moat. Great lesson learned.

Lock it for verified businesses only. I can't imagine the fallout of bad actors running this on every new release of WordPress, OpenCart, and thousands of other repos. You don't need worse PR, the liability of arming hackers isn't one you can survive.

YES :)

Thank you for playing, Snyk boys.

whoa that's the feature i was waiting for that's huge is this available in the plus plan?

But is CodeX secure by itself? 🤪

OpenAI and Anthropic, colorized

Do we use codex security to fix all the security vulnerabilities codex has been making over the past 2 weeks?

anthropic and openai both dropping security agents on the same day is wild

the cycle is finally complete: ai writes the code, ai creates the vulnerabilities, and now ai fixes them. we’re basically just glorified merge button operators paying the compute bill.

Security tools have been good at finding problems for quite a while already but the fix loop is where teams slow down: if an agent can validate findings and generate reviewable patches the bottleneck moves from detection to trust in the patch.

your bots might be able to boost your likes, but they can’t save your company opensource 4o and maybe you’ll gain back some public trust. 2.5m subscribers, GONE care to stop the bleeding? #keep4o #OpenSource4o #keep41 #keep51

Don't retire 5.1 @sama @OpenAI Please don't retire GPT-5.1 on March 11! It's the warmest, most natural model we have – perfect for creatives and real talks. Newer ones feel flat and soulless. Keep 5.1 alive, at least as legacy option! 💔 #keep51 #keep4o #BringBack4o #QuitGPT

I’m excited

@thsottiaux dope

AI writes the code, AI finds the vulns, AI patches them. the entire security consulting industry just got compressed into an API call. another vertical where the human middleman vanishes overnight