Загрузка видео...
Не удалось загрузить видео
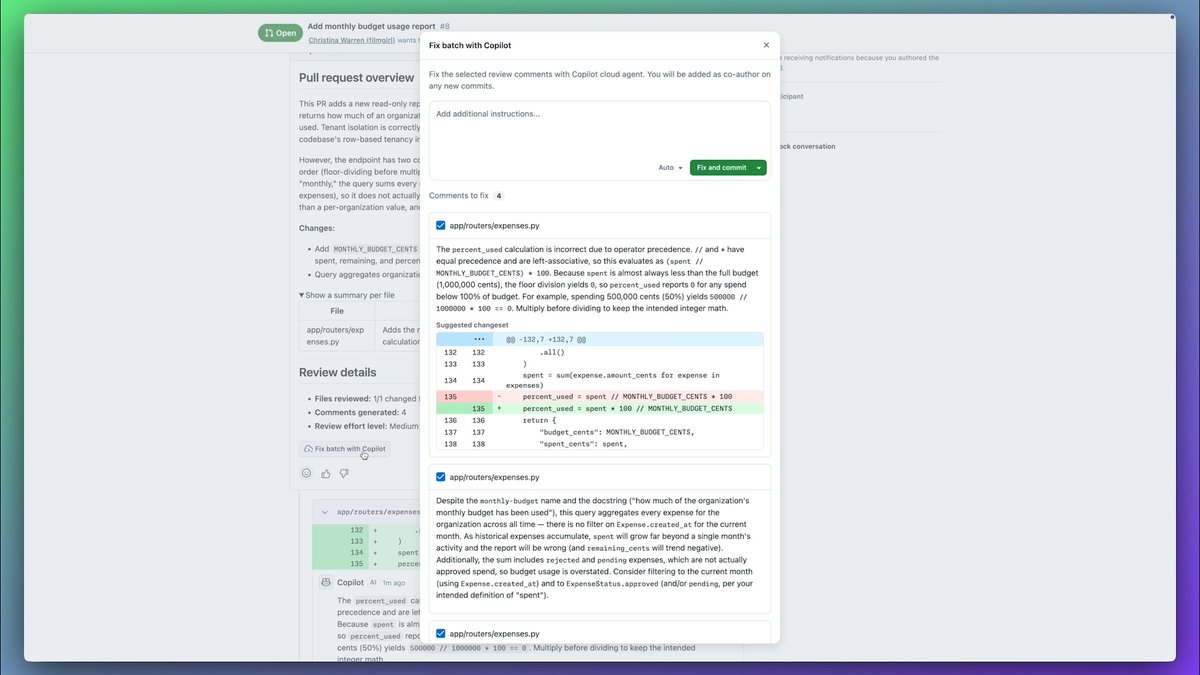
Now in research preview: Codex Security Review It takes a deeper look at GitHub pull requests for security issues, using repository context to surface actionable findings directly in the PR. See how to enable automatic reviews:

306,211 просмотров • 3 месяцев назад •via X (Twitter)
Комментарии: 34

Give 4o back to us 😒 #keep4o #OpenSource4o #GPT4o

@dkundel Codex Security Review taking a deep look at GitHub pull requests 😂

Now maybe give us what we actually want 4o. Try listening please. #4oForAll

the useful receipt is downstream: which finding changed code, which was suppressed with a reason, and whether the same weakness escaped later, because review volume alone cannot prove security value.

Research preview on a security tool is where trust goes to die. If it misses one real vulnerability or floods devs with noise, teams will disable it in a week and never turn it back on. The bar here is way higher than "interesting demo."

No more “it works on my machine… and also has a high-sev vuln” moments. Can’t wait to enable automatic reviews.

This is actually useful. Security reviews directly on the PR could save a lot of time, especially if Codex already understands the full repo context

Having the findings right in the PR is much nicer. Switching to another tool just to review security usually gets pushed until later

At present, neither the Codex team nor ChatGPT can reliably identify this failure mode without independent human artifact inspection. Based on the current public state of AI evaluation infrastructure, Japan cannot reliably detect it either.

Bro, GitHub is down today. I guess didn’t pass the review process

How are you going to roll that into Codex source code without GitHub though

having security findings directly in the pr is actually useful most tools still make you dig for this stuff

The comments on this one are gonna be good.

cybersecurity is developing so far, openai and top github repos confirm it lol

security review that actually reads the repo not just the diff. pr bots just got interesting

Inline findings are useful only if developers trust the signal-to-noise ratio. Repository context could beat generic security scanning. Precision will decide adoption. @TechImpactTV

Yo dude @trq212 @ClaudeDevs @claudeai why is this feature not with Claude??

"During the introductory period, Security Review does not consume ChatGPT credits. Usage limits may apply." The separate tracking of credits and weekly limits in analytics is confusing me. Does this mean the weekly limit won't decrease, but that if you use security review too much, you'll hit a something threshold?

Interesting... I applied to the program and I am now approved... Will test it thoroughly

Won't the security review trigger the Codex cybersecurity guardrails? It has already done that for me on a number of occasions.

I had a problem, I couldn’t enter the payment address to be able to make my purchase so I used my iPhone to be able to make the purchase and I looked carefully, I connected you well to my personal account, I noticed that Apple generated a temporary email to be able to make the purchase. So paying on a new account, I want to transfer this account to my old account because it is there that I have all my conversations and I have all my memories. It is really very urgent for me. If you can do it now, I don’t know any access to that account, I don’t want to use it, I want to use my personal email. [email protected]

Go team! 🛡️

Security findings become more actionable when each comment identifies the untrusted input, the permission boundary it crosses, and the code path that makes exploitation reachable.

tried this on a PR last week, caught a sql injection i missed. kinda scary

so does this mean the repo context actually matters for catching real issues or is it just another automated gatekeeper

Codex schaut jetzt also nicht nur auf Code, sondern auf den ganzen PR-Kontext. 😏 Aus „Sieht sicher aus“ wird langsam „Zeig mir bitte, warum es sicher ist.“ Die Security-Abteilung bekommt offenbar endlich einen Kollegen, der Pull Requests freiwillig liest.

PR context can make findings actionable, but the product outcome is the closed loop: finding, exploit path, severity, owner, proposed fix, review, regression test, merge decision, and later retest. Security review earns trust when it proves risk retired, not alerts produced.

the constraint that makes a PR wrong usually lives in an issue thread, not in the tree.

The future of AI coding is not just writing code faster, but helping developers build more reliable and secure software.

The repo context piece is the key part here. A lot of security issues in PRs only show up when you know what the surrounding code already trusts or checks. Curious how it handles cases where the vulnerability sits in a dependency call two files away from the changed lines.

why aren't security reviews built into every code review? seems like it's a core job of examining the changed code to identify if it introduced any security vulnerabilities?

we should celebrate this @thsottiaux

False positives are gonna be insane if context window misses legacy repo rule

Repository context could make security review more actionable than generic scanners.