Video wird geladen...
Video konnte nicht geladen werden
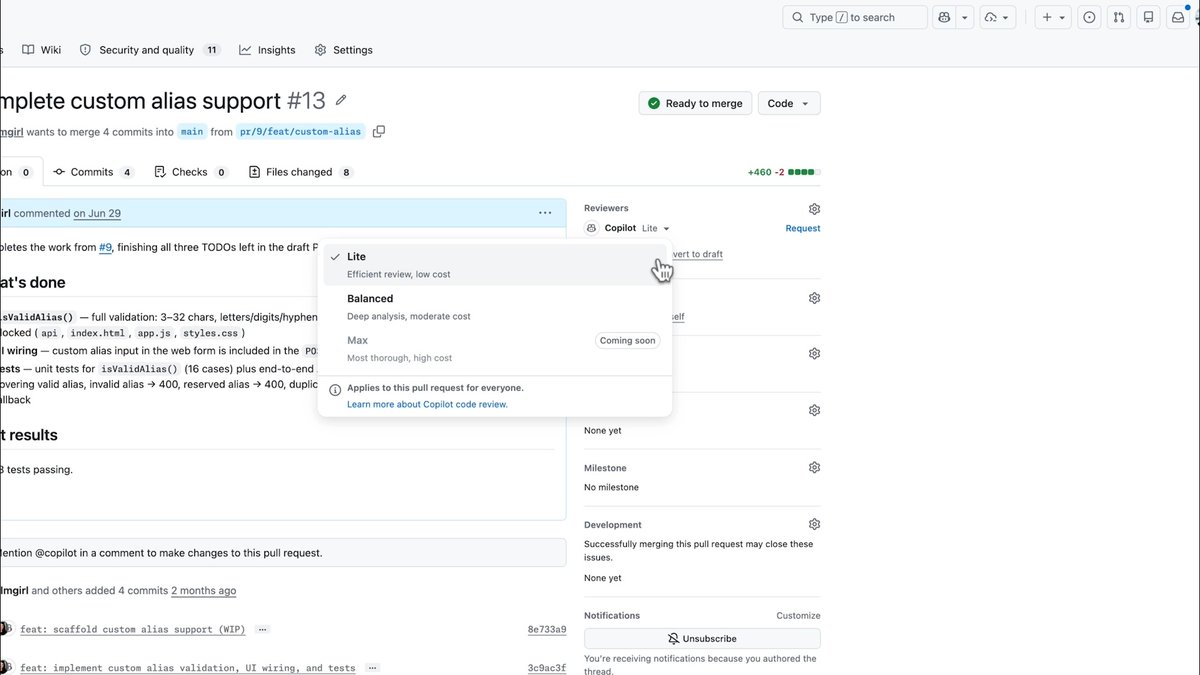
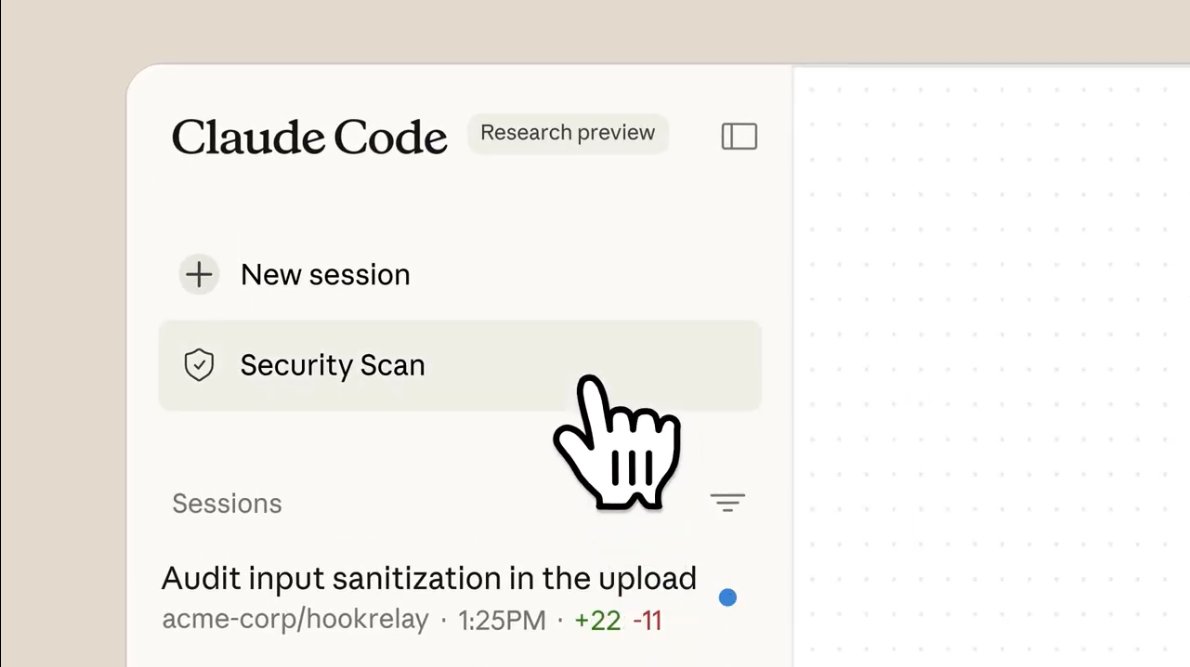
We just shipped automated security reviews in Claude Code. Catch vulnerabilities before they ship with two new features: - /security-review slash command for ad-hoc security reviews - GitHub Actions integration for automatic reviews on every PR
1,262,042 Aufrufe • vor 1 Jahr •via X (Twitter)
38 Kommentare

The /security-review command runs security analysis directly from your terminal. Claude checks for vulnerabilities like: - SQL injection risks - XSS vulnerabilities - Insecure data handling Found a vulnerability? Simply ask Claude to fix it.
Our new GitHub action is a friendly security reviewer for all your PRs. When configured, the integration checks every new PR for vulnerabilities, posting inline comments with explanations and recommended fixes.
We’re using this ourselves at @AnthropicAI. It's already caught real vulnerabilities, including a potential remote code execution vulnerability in an internal tool. With the GitHub action, we were able to fix it before it made it to production.
Getting started: For the /security-review command, simply update Claude Code and run the command. For the GitHub action, view our docs to get started:

this is F*N amazing. You just killed 10 security startups though 😂

cybersecurity is now irrelevant

Using Claude to fix issues with new Claude tools 🤯

the "just ask claude to fix it" part is what gets me though. like yeah it'll catch the obvious stuff (sql injection, xss) but security fixes aren't always straightforward. sometimes you need to rethink the whole approach, not just patch the immediate vulnerability still, for catching low-hanging fruit this could save a ton of time. beats manually auditing every input validation

Smart move! Automation keeps security tight and devs sane.

here’s what every dev team actually wants in prod: something that saves us from our own code at 2am. this is the good stuff. security by default is underrated.

This is so so so huge, people don't even realize

Fantastic, I've been manually dong this is "ultrathink" prompt with sub-agents. This is huge. 🙌

This is dope and much needed! Trying it out now!

Claude: catching bugs before they become ‘features’.

claude code is the new startup killer

did coderabbit become obsolete at this point?

olha isso aqui @sushicomabacate

@coderabbitai sweating

PR reviews via gh actions is my favourite feature. Caught several non trivial bugs, that were left out in the PRs.

security reviews just went from "we'll fix it later" to "fix it now or the robot judges you" 😅

Thanks but my app can't get exploited if it has no users anyway.

Super valuable. Thank you! ✨

Tea coulda used this

Even better when paired with @thesysteminit - use it to find and fix security issues in your infrastructure.

sybersec go brrr

oh wow,, Anthropic ships non stop. will OPUS OS be in collaboration with Anthropic Claude for the blockchain based agentic ecosystem ??? @opus_genesis

It's amazing for catching standard security vulnerabilities.

Not bad for a project with 50k LoC written almost entirely with Opus&Sonnet.

One step closer to secure vibes!

Check that @saradietschy you gonna love it

AppSec vendors about to unfriend Claude.

@CPunella 👀

Damnn @claudeai killed potential security based startups

Oh come on, I was gonna take a break a bit from coding during vacation. I guess I’ll have a Quick Look….

@ Tea

@PQPEGASPARI bro 💀

Security on autopilot! GitHub Actions integration should make our dev life easier and our code much safer. Cheers to Claude Code!

!submit @curatedotfun #ai