正在加载视频...
视频加载失败
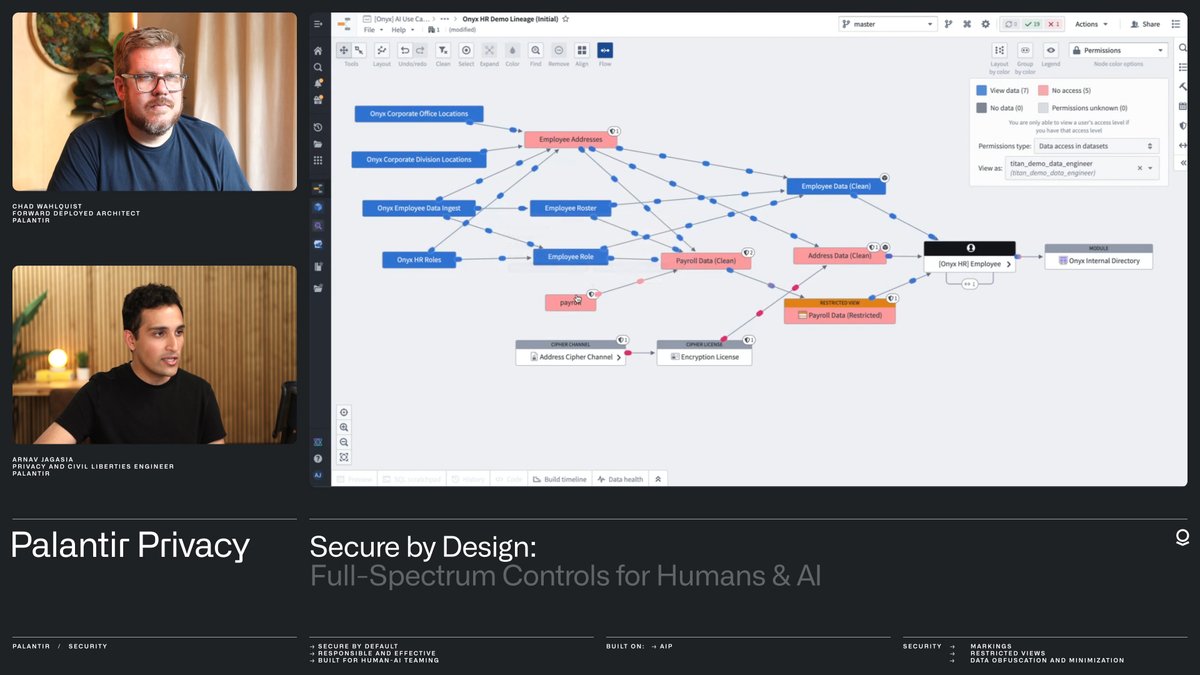
introducing PII Guard 2.0. protect user privacy, without compromising observability. now with role-based access, audit logs, and more granular controls. only in Raindrop - i'm very proud of this ship.🧵
76,103 次观看 • 2 个月前 •via X (Twitter)
30 条评论

it might be hard to believe, but with every other AI observability platform, companies just log all raw traces. names, health conditions, phone numbers, emails... anyone in the company with any justification to understand the health of the product can see it all.
while we believe present circumstances often require PII to debug specific issues, we believe it's in the best interest of users and companies alike to: 1. Lock down access by role. Most people never need to see raw PII. The few who do should be explicitly granted it.
2. Audit access. When someone does reveal PII, that should leave a record: who, what, and when. 3. Control sensitivity. Not all PII is equal. A phone number and the name of a company are not the same. PII Guard does all 3.
in the future, companies should be able to improve their AI products without ever seeing sensitive information from users. we are actively building that future too. in the meantime, we want to make sure that sensitive data is seen by as few people as absolutely necessary.
try it today at

@raindrop_ai Great to see someone in the trace / data collection world care about this, nice stuff!
@raindrop_ai thanks, its not the sexiest/most viral thing to launch, but we care.

@raindrop_ai Nice work on this, guys. This is a massively underserved enterprise requirement.
@raindrop_ai thanks we agree

@raindrop_ai one of the things i hated MOST about observability in general. great great ship :) will make our users much happier

@raindrop_ai legit very cool
@raindrop_ai thank you!

@raindrop_ai Yea this is really smart, will be standard eventually
@raindrop_ai i hope so!
@raindrop_ai Would absolute love if my provider had this right now.
@raindrop_ai dm me, we make it easy to switch :)

@raindrop_ai This is really smart

@raindrop_ai Super cool! Very hard and annoying to solve, congrats

@ycombinator @raindrop_ai is this a challenge?

@raindrop_ai neat - could you share how does this actually works? regex or simple LLM? like i imagine either way you're going to have a false positive / false negative rate of some sort, seems like a tradeoff with no perfect solution
@raindrop_ai very much not regex. it is all ML based. re: false positives/false negatives, we give our customers the option to control sensitivity for this very reason. strict mode will have very very very few false negatives.

@raindrop_ai Did you guys train a PII masking model or use an existing one?

@raindrop_ai Hey! You should have a look at

@raindrop_ai redaction at ingest beats scrubbing later

@raindrop_ai lezgooooo

@raindrop_ai Since this is a managed offering and not open source you’re telling us that we’re expected to transmit the data to you first and then have you redact it server side on your end? Why would anyone do that over using Microsoft Presidio and OpenAI Privacy Filter locally client-side?
@raindrop_ai We do have an on-prem redaction offering for enterprise. tldr; it's often easier for teams, and the only way when you want role-based access to PII
@raindrop_ai Except that’s not true because we handle it with ATR claims through Panguard. It’s not tightly coupled to the redaction engine but it permits role based access for local only deploys I just feel like you need a big disclaimer or warning sign if suggesting people to send data out
@raindrop_ai Sorry I'm really not following. The default right now is that many teams send all of their PII to their hosted observability platform. You might not, and that's great! Some teams NEED PII in order to debug their agent. This makes PII data more secure with one click.
Tbh I did not realize that that was the default for most companies. I’ve always considered that bad practice. I did more research since you mentioned this though and yeah it’s rather extremely common and many providers like datadog etc offer to redact it on their side. So you’re improving on the baseline then but should really push the on-Prem option a lot more imo. Educate people on why they shouldn’t default to sending it out because it’s really not ideal