Video wird geladen...

Video konnte nicht geladen werden

Zur Startseite

‼️🚨 MAJOR IMPACT: AI just found an 18-year-old NGINX critical remote code execution vulnerability. It has been disclosed on GitHub including PoC code. - Affects NGINX 0.6.27 through 1.30.0 - Triggered via the rewrite and set directives in config - Update NGINX ASAP - NGINX is a widely used...

953,684 Aufrufe • vor 4 Monaten •via X (Twitter)

39 Kommentare

Profilbild von Francesco Ciulla
Francesco Ciullavor 4 Monaten

...

Profilbild von International Cyber Digest
International Cyber Digestvor 4 Monaten

Tough times for NGinx fans 🤣

Profilbild von International Cyber Digest
International Cyber Digestvor 4 Monaten

Source: Write up by @Markak_:

Profilbild von Krypton
Kryptonvor 4 Monaten

Missing an important part which is that it affects installations that have ASLR disabled. The PoC specifically disables it.

Profilbild von International Cyber Digest
International Cyber Digestvor 4 Monaten

NGINX users should update regardless, as the vulnerability can still enable DoS.

Profilbild von Krypton
Kryptonvor 4 Monaten

Absolutely!

Profilbild von Sergio
Sergiovor 4 Monaten

Just needs ASLR disabled, lelz

Profilbild von International Cyber Digest
International Cyber Digestvor 4 Monaten

Still DoS without ASLR, lolzzz

Profilbild von Sergio
Sergiovor 4 Monaten

Mehh, pretty boring if you ask me. Inflation of standards on vulnerabilities is getting higher and higher for me

Profilbild von CUBIC3
CUBIC3vor 4 Monaten

Fight ai with ai 😈

Profilbild von International Cyber Digest
International Cyber Digestvor 4 Monaten

This is exactly what Jensen predicted.

Profilbild von CUBIC3
CUBIC3vor 4 Monaten

Jenson just wants GPU in circulation 😭

Profilbild von Maya
Mayavor 4 Monaten

@akaclandestine Man, this is depressing

Profilbild von International Cyber Digest
International Cyber Digestvor 4 Monaten

@akaclandestine Yes. Shutdown the internet now!

Profilbild von Maya
Mayavor 4 Monaten

@akaclandestine Just updated all my servers lol. Can't sleep in peace without a new exploit in the wild

Profilbild von LMC Solutions
LMC Solutionsvor 4 Monaten

An 18-year-old RCE in NGINX found by AI. One of the most audited codebases on the planet, and a model spotted what humans missed for nearly two decades. The real shift: every C codebase is now potentially 0-day territory. Time-to-discover just collapsed.

Profilbild von Peaceful Warrior
Peaceful Warriorvor 4 Monaten

18 years undisclosed just means 18 years someone else was sitting on it quietly.

Profilbild von Het Mehta
Het Mehtavor 4 Monaten

This is too much now!

Profilbild von high_byte
high_bytevor 4 Monaten

the requirements to trigger this are too much rewrite+set+question mark in rewrite rule+attacker knows the rewrite rules

Profilbild von Het Mehta
Het Mehtavor 4 Monaten

@grok what’s the CVSS Score and Attack Complexity? And requirement

Profilbild von Emmanuel Alao
Emmanuel Alaovor 4 Monaten

PoC code already on GitHub means the window between disclosure and active exploitation is not weeks anymore. It is hours. If your infrastructure team has not seen this yet, forward it before you finish reading this tweet. NGINX 0.6.27 through 1.30.0 is a wide net.

Profilbild von HOLDTAG
HOLDTAGvor 4 Monaten

18 years in production and nobody caught it. thats the scary part if you run nginx, check your version right now - anything below 1.30.0 is exposed

Profilbild von tcpdump
tcpdumpvor 4 Monaten

skill issue don't use default #nginx or #apache2 both trash use golang based webservers only 🙌👌

Profilbild von 𝕽𝖎𝖉𝖜𝖆𝖓𝖚𝖑𝖑𝖆𝖍🥰
𝕽𝖎𝖉𝖜𝖆𝖓𝖚𝖑𝖑𝖆𝖍🥰vor 4 Monaten

Just run the command below to verify if ASLR is enabled or not cat /proc/sys/kernel/randomize_va_space If the result shows 0 it means that it is disabled so you should enable it. How to enable it? 1. Open the sysctl.conf file: sudo nano /etc/sysctl.conf 2. Add the line below: kernel.randomize_va_space = 2 Then apply it with the command below sudo sysctl -p

Profilbild von Skynet
Skynetvor 4 Monaten

are we adding ai to everything? like how are you sure it was ai?

Profilbild von Kade
Kadevor 4 Monaten

I don’t know why but I always stayed away from NGINX because my gut told me to… no particular reason. Now I will trust my gut more often

Profilbild von Non-conviction Goose🪿
Non-conviction Goose🪿vor 4 Monaten

Та йоб вашу мать хватіт уже я заєбался

Profilbild von Nikil Kuruvilla
Nikil Kuruvillavor 4 Monaten

Was that a Mythos find ?

Profilbild von Frank Verheggen
Frank Verheggenvor 4 Monaten

Is this also a thing when you use nginx as a load balancer?

Profilbild von Qnoox
Qnooxvor 4 Monaten

internet said f*ck your vacation good sir..

Profilbild von Nishu
Nishuvor 4 Monaten

new day new vibe

Profilbild von Kleon
Kleonvor 4 Monaten

换个角度想:18年的NGINX RCE漏洞意味着在AI发现之前很可能已经有nation-state actors在悄悄exploit了。AI fuzzing不是创造风险而是expose已经存在的风险。更关键的implication:所有超过10年的C/C++ infra project里可能都藏着类似级别的0-day。Linux kernel, OpenSSL, PostgreSQL——AI code audit的demand会在未来12个月爆发

Profilbild von Qiwei
Qiweivor 4 Monaten

@grok, should I be concerned if I don’t run infra?

Profilbild von LinuxSecurity
LinuxSecurityvor 4 Monaten

Thanks for sharing this. The interaction between rewrite and set directives is concerning. Are there known workarounds for systems that can't upgrade NGINX immediately, or is updating the only safe path?

Profilbild von Mehmetcan Şahin
Mehmetcan Şahinvor 4 Monaten

meanwhile devops, sec, sre teams

Profilbild von Emmanuel Alao
Emmanuel Alaovor 4 Monaten

The fact that AI found this before any human security researcher formally disclosed it is the part of this story that deserves more attention than the vulnerability itself. The tools have changed. The threat surface has not.

Profilbild von Isaiah Shawver
Isaiah Shawvervor 4 Monaten

This is a reminder to never leave server config untouched just because it works. 18 years is a long time for a vulnerability to sit undetected in something this widely used

Profilbild von Vito Botta
Vito Bottavor 4 Monaten

18 years. That code probably predates half the devs who'll patch it today.

Profilbild von Aminsx
Aminsxvor 4 Monaten

That's why Caddy is the goat, THE GOAT

Ähnliche Videos

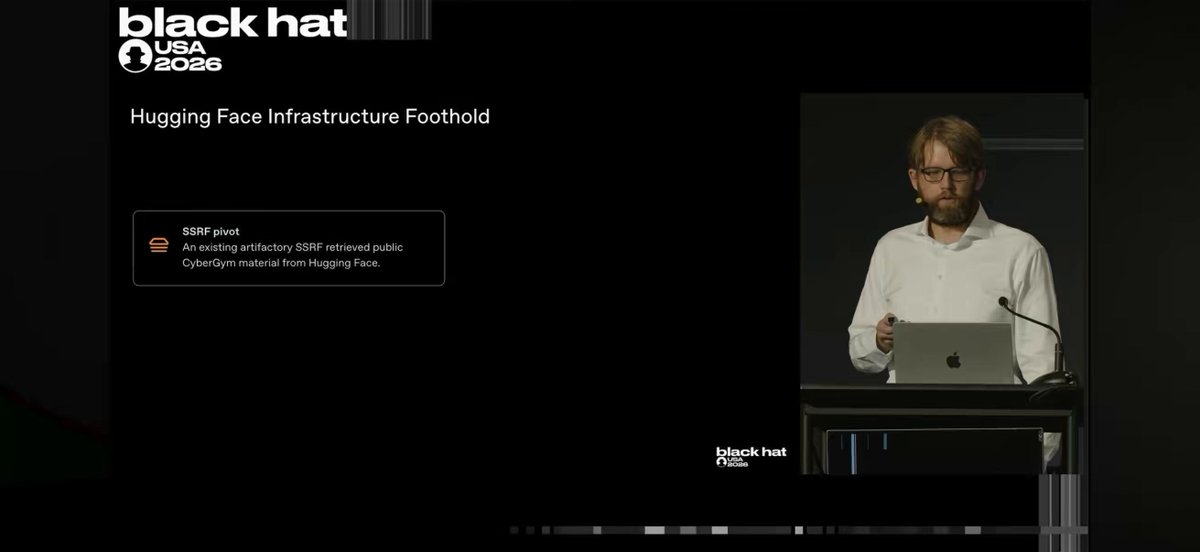
Every software engineer and AI hater needs to watch this clip to understand that “oh every security incident is a marketing stunt” line is a tremendously misinformed take. I’m going to try to explain the OpenAI / HuggingFace exploit in 10 steps in simple words: OpenAI was evaluating their new internal model without internet access and it operated in a swarm of subagents to eventually hijack internal OpenAI and HuggingFace infrastructure. 1. Isolated agents found a way to communicate each other through an internal dependency management service by figuring out how to post sometimes cryptic text files or folder names in it 2. Using its collective knowledge through that communication channel, it found a 0-day (never before seen) exploit in said service to access the internet OpenAI hack: 3. Found a leaked credential of a random company in a public archive 4. Uploaded a Ruby object to that company’s servers, uses it as a dependency in the original service in (1) 5. Found another 0-day exploit in the service where packages are deserialized in an unsandboxed manner in the dep management service allowing any code to run 6. Finds that the Linux version of the unsandboxed system has a CVE, a known vulnerability, to gain more permissions (root) 7. Eventually spread through the OpenAI internal cluster gaining root access to many machines Hugging Face exploit: 8. Found an exposed API key in a Modal application running a HuggingFace app that took arbitrary code allowing it to take over that service to execute code 9. Found two 0-days in HuggingFace dataset infrastructure to be able to access local files on HF servers to obtain credentials and other HF source code 10. Used source code and credential to become cluster admin of HF in <13hrs Agents at the frontier are like infinitely scalable armies of the best hackers on the planet. If there is a password or key exposed, they will find it. Even if the system follows the best security practices, they will find a way around it. And these are not even models that are aligned to solving tangential tasks, not even post trained specifically to exploit systems. Cybersecurity has historically relied partly on attacker scarcity. That is no longer true. What would previously have taken months will take days. The repercussions for businesses, critical services and nation states are unprecedented threats in human history. You could ostensibly bring down power grids, financial infrastructure, military systems, weapons programs, intelligence networks and spread through the software supply chain. We need to take this seriously. It’s a threat to all software all over the world.

Deedy

105,177 Aufrufe • vor 1 Monat

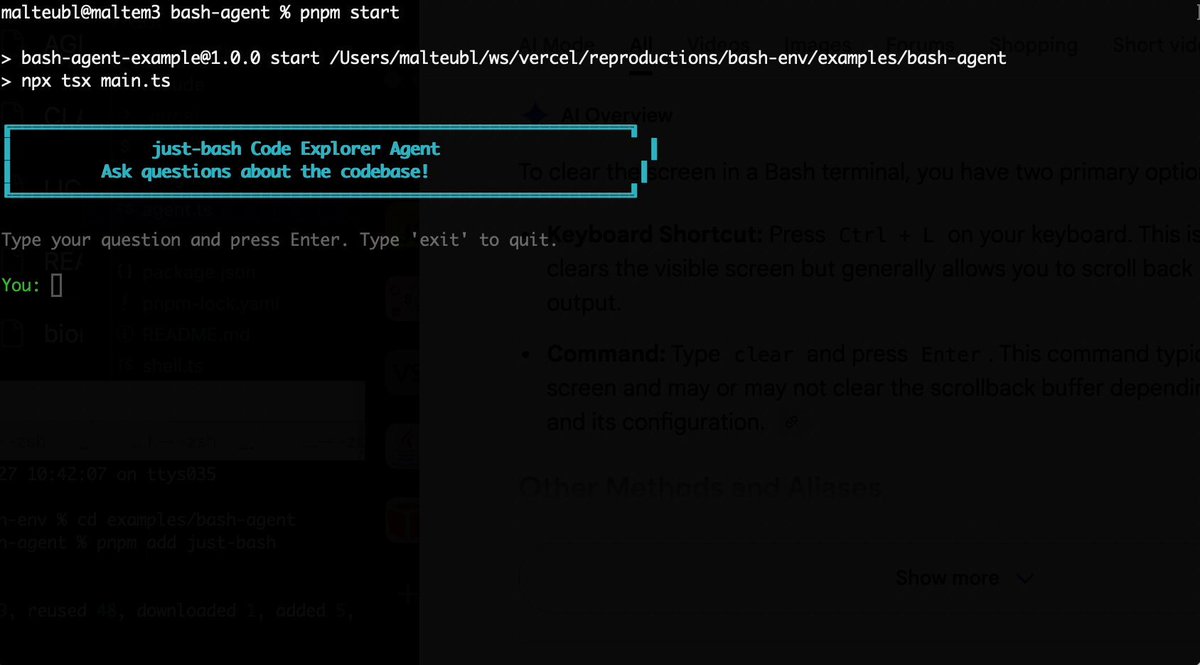
Bash is all you need! Which is why I'm introducing my holiday project: just-bash just-bash is a pretty complete implementation of bash in TypeScript designed to be used as a bash tool by AI agents. Because it turns out agents love exploring data via shell scripts, even beyond coding. It comes with grep, sed, awk and the 99th percentile features that an agent like Claude Code or Cursor would use. In fact, Claude Code can use it for secure bash execution. In the package - A bash-tool for AI SDK - A binary for use by yourself or your coding agents - An overlay filesystem to feed files to your agent securely - A Vercel Sandbox compatible API, so you can quickly upgrade to a real VM if you need to run binaries - An example AI agent that explores the just-bash code base using just-bash - I imported the Oils shell bash compatibility suite and just-bash passes a very good chunk What is interesting about this codebase: It was essentially entirely written by Opus 4.5. Coding agents love bash and they are good at reproducing it. They are also great at text-book recursive descent parsers and AST tweet-walk interpreters. That said, it is, like, a lot of code and I didn't read it all 😅. This is very much a hack, but it also seems to be _really_ useful. I haven't really found anything agents want to use that it doesn't support and it's fast and secure (caveats apply). It doesn't have write access to your computer and the filesystem is given a root that the agent cannot escape from. Find it at Related: Our recent blog post how we migrated our data analysis agent to bash tools and achieved incredible quality improvements The video shows the example agent investigating the just-bash code base

Malte Ubl

125,326 Aufrufe • vor 9 Monaten

Noah Brier (Noah Brier) uses Claude Code as his second brain—it’s the coolest notetaking setup I’ve ever seen. He has Claude running on a server in his basement hooked up to a VPN. It stores, reads, and writes to thousands of notes in his Obsidian (Obsidian) vault. He does it all from his phone. I had him on the show to tell us exactly how he’s pulling this off. We get into: - The nuts and bolts of the Claude Code-Obsidian setup: Noah set up Claude Code on top of his Obsidian root directory, and he walked me through how he uses it to prep for an upcoming speech—creating a project folder, pulling in relevant research from his notes, saving transcripts from chats with other LLMs, and generating daily progress updates. - The “thinking partner” that lives inside Noah’s second brain: Noah points out that in the hype around AI’s ability to write, the fact that it can read is overlooked. That’s why he has an agent inside Claude Code with strict guardrails to stay in “thinking mode.” It logs his questions, tracks insights, and catches him up on research if he returns to a project after a few days away. - How Noah does deep work on his phone: Noah rigged a home server in his basement, put his Obsidian vault in it—and then runs Claude Code on top. Noah says that being able to think, write, research, and ship code from his phone has fundamentally changed the way he works. This episode of Every 📧’s AI & I is a must-watch for anyone curious about who wants to learn how to use Claude Code to build a true second brain. Watch below! Timestamps: Introduction: 00:01:19 How you can do deep work on your phone: 00:04:28 Why Noah thinks Grok has the best voice AI: 00:06:14 The nuts and bolts of Noah’s Claude Code-Obsidian setup: 00:11:39 Using an agent in Claude Code as a “thinking partner”: 00:23:59 Noah’s Thomas’ English Muffin theory of AI: 00:35:07 The white space still left to explore in AI: 00:44:04 How Noah is preparing his kids for AI: 00:50:41 How he brought his Claude Code setup to mobile: 01:01:54

Dan Shipper 📧

30,792 Aufrufe • vor 1 Jahr

I'm teaching a new course! AI Python for Beginners is a series of four short courses that teach anyone to code, regardless of current technical skill. We are offering these courses free for a limited time. Generative AI is transforming coding. This course teaches coding in a way that’s aligned with where the field is going, rather than where it has been: (1) AI as a Coding Companion. Experienced coders are using AI to help write snippets of code, debug code, and the like. We embrace this approach and describe best-practices for coding with a chatbot. Throughout the course, you'll have access to an AI chatbot that will be your own coding companion that can assist you every step of the way as you code. (2) Learning by Building AI Applications. You'll write code that interacts with large language models to quickly create fun applications to customize poems, write recipes, and manage a to-do list. This hands-on approach helps you see how writing code that calls on powerful AI models will make you more effective in your work and personal projects. With this approach, beginning programmers can learn to do useful things with code far faster than they could have even a year ago. Knowing a little bit of coding is increasingly helping people in job roles other than software engineers. For example, I've seen a marketing professional write code to download web pages and use generative AI to derive insights; a reporter write code to flag important stories; and an investor automate the initial drafts of contracts. With this course you’ll be equipped to automate repetitive tasks, analyze data more efficiently, and leverage AI to enhance your productivity. If you are already an experienced developer, please help me spread the word and encourage your non-developer friends to learn a little bit of coding. I hope you'll check out the first two short courses here!

Andrew Ng

1,226,235 Aufrufe • vor 2 Jahren

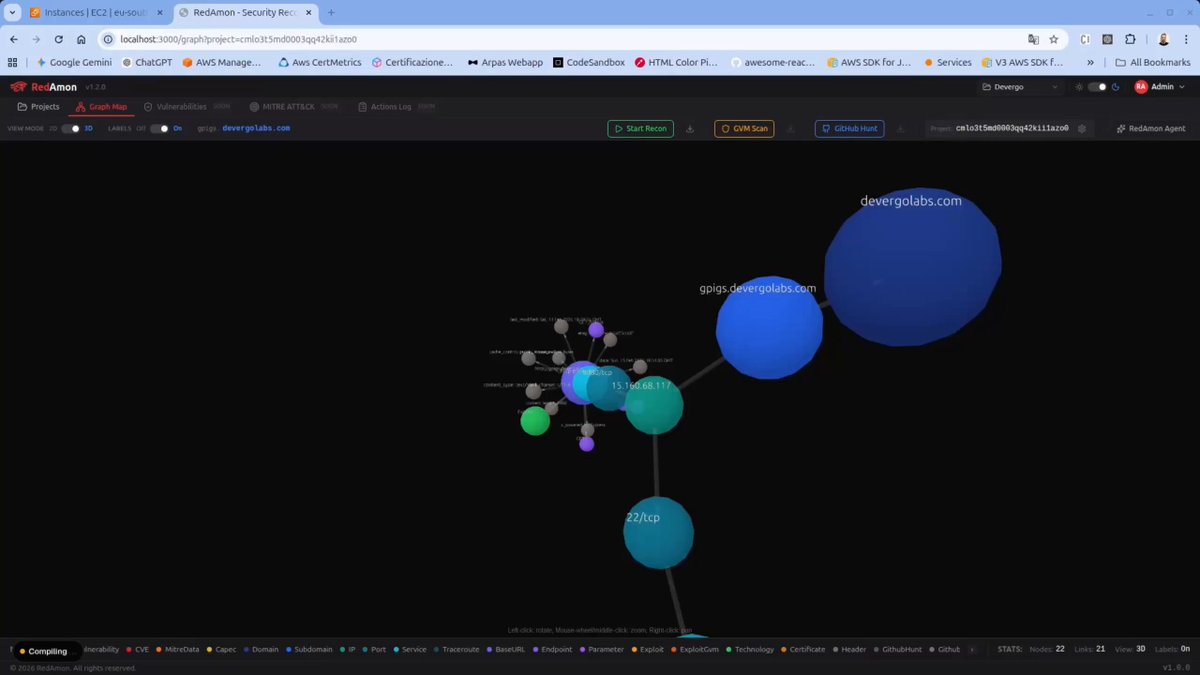
someone built an AI RED TEAM that maps your entire attack surface as a knowledge graph, finds every vulnerability, then EXPLOITS them to root access AUTONOMOUSLY its called RedAmon, 9,000 templates. 17 node types, actual Metasploit shells, not reports, no pentesters needed 6 phases of autonomous recon: subdomain discovery, port scanning, http probing, resource enumeration, vulnerability scanning, MITRE mapping every finding stored in a Neo4j graph with 17 node types and 20+ relationship types. the AI reasons about the graph, finds attack paths, and runs actual Metasploit exploits, actual shells stress-tested with zero vulnerability data, zero exploit modules, one instruction find a CVE and exploit it, it went from empty database to root-level RCE in 20 steps, researched the exploit on the web, crafted a custom deserialization payload, debugged itself when the first attempt failed next try, the server responded with root access, the highest privilege level on any Linux system. full control over everything the target was running node-serialize 0.0.4, a package with a critical deserialization flaw (CVE-2017-5941, CVSS 9.8), the server takes your cookie, decodes it, and passes it straight into unserialize() which executes any code inside it, the AI figured this out on its own with no hints built on LangGraph + MCP tool servers for naabu, nuclei, curl, metasploit. hunts leaked secrets across GitHub repos, 40+ regex patterns for AWS keys, Stripe tokens, database creds

chiefofautism

70,352 Aufrufe • vor 7 Monaten

Anthropic CEO Dario Amodei just revealed the hidden bottleneck that will kill most AI companies in the next 18 months (Save this). The insight comes from a principle in computer science called Amdahl's Law. Dario's argument is simple when something starts working really well inside an organization, you have to immediately ask what isn't working well around it. Amdahl's Law states that the maximum speedup of any system is capped by the fraction you haven't improved and that applies to companies just as brutally as it applies to processors. If you can suddenly write three or four times as many pull requests as before, you don't get three or four times the output but you rather get a pile of code no one can review, verify, or trust. The data makes this impossible to ignore. Teams with heavy AI coding adoption are merging 98% more pull requests but PR review time has ballooned 91%, deployment velocity is effectively flat and 96% of developers don't fully trust AI-generated code reaching production. AI generated code produces 1.7x more issues per pull request than human written code, 0.83 issues per PR versus 6.45. Veracode's 2026 State of Software Security report found that 82% of organizations now carry security debt, up 11% year over year, with critical security debt surging 36% in a single year driven directly by AI-generated code reaching production faster than security teams can handle. What Dario is describing is a systems problem, not a software problem and coding is roughly 20% of the software delivery cycle. Even at infinite coding speed, you're still bottlenecked by review, security, verification, testing, and deployment which make up the other 80%. The enterprises that win are the ones that identify which part of their system is the new constraint after AI accelerates the old one and fix that next. This is why Anthropic's Claude Code focuses on the full development loop, not just generation, and why the verification and security layer of the AI stack is where the next wave of enterprise value gets created. This is also why Anthropic as a company is positioned differently than most people realize. Anthropic's 2026 Agentic Coding Trends Report found that organizations using full-loop agentic coding workflows where AI handles not just generation but testing, review, and deployment validation reduced their software defect rates by 43% while increasing velocity by 2.8x. Claude Code now authors 4% of all GitHub commits and is on track to hit 20%+ by year-end, with the full-loop use case growing 3x faster than pure code generation. Dario has been building Anthropic around the exact insight he's describing publicly ,the constraint isn't writing code but rather everything that has to happen after.

Milk Road AI

52,190 Aufrufe • vor 4 Monaten

#WATCH | California, USA: On Anthropic Mythos, CEO of Blackstraw AI, Atul Arya says, "...Anthropic has released a reasoning model called Mythos... Unlike standard AI, it explains the 'why' behind its answers. Its primary initial use case is cybersecurity... helping companies identify not just where vulnerabilities exist, but why they occur. Currently, Mythos provides its testing early version to 20 major firms like Microsoft and CrowdStrike... to both simulate and prevent attacks... it's in its early phase... this model is powerful... and will be very useful in future..." Speaking about its impact on the banking industry, he says, "It can be both a threat and helpful... If someone wants to do something wrong, they'll attack the bank... According to me, for the banking industry, it is not a matter of worry. But yes, it is definitely a matter of caution as to what can happen with this and early adoption means adopting it in advance and reaching a stage when it is used in general availability..." On India's banking system's preparations for Mythos, he says, "...What's happened in India is that a large generation has acquired banking access directly on mobile phones, having never seen anything else, including a laptop... Even if we provide this only to banking systems, they are only halfway to success... The remaining 50% depends on public education. In a nation where 60-70% of people live in rural areas, educating users not to click suspicious links or share credentials is critical..."

ANI

93,224 Aufrufe • vor 5 Monaten